 filings.tools
Fortinet 10-K 2021-12-31
Filed 2022-02-25. 23 sections, 529K characters. Original on sec.gov · Markdown · JSON
Cover and table of contents
UNITED STATES
SECURITIES AND EXCHANGE COMMISSION
Washington, D.C. 20549
FORM 10-K
(Mark One)
| ☒ | ANNUAL REPORT PURSUANT TO SECTION 13 OR 15(d) OF THE SECURITIES EXCHANGE ACT OF 1934 |
For the year ended December 31, 2021
or
| ☐ | TRANSITION REPORT PURSUANT TO SECTION 13 OR 15(d) OF THE SECURITIES EXCHANGE ACT OF 1934 |
For the transition period from to
Commission file number: 001-34511
FORTINET, INC.
(Exact name of registrant as specified in its charter)
| Delaware | 77-0560389 | ||||
| (State or other jurisdiction of incorporation or organization) | (I.R.S. Employer Identification No.) |
899 Kifer Road
Sunnyvale, California 94086
(Address of principal executive offices, including zip code)
(408) 235-7700
(Registrant’s telephone number, including area code)
Securities registered pursuant to Section 12(b) of the Act:
| Title of each class | Trading Symbol | Name of each exchange on which registered | ||||||||||||
| Common Stock, $0.001 Par Value | FTNT | The Nasdaq Stock Market LLC |
Securities registered pursuant to Section 12(g) of the Act: None
Indicate by check mark if the registrant is a well-known seasoned issuer, as defined in Rule 405 of the Securities Act. Yes ☒ No ☐
Indicate by check mark if the registrant is not required to file reports pursuant to Section 13 or Section 15(d) of the Act. Yes ☐ No ☒
Indicate by check mark whether the registrant (1) has filed all reports required to be filed by Section 13 or 15(d) of the Securities Exchange Act of 1934 (“Exchange Act”) during the preceding 12 months (or for such shorter period that the registrant was required to file such reports), and (2) has been subject to such filing requirements for the past 90 days. Yes ☒ No ☐
Indicate by check mark whether the registrant has submitted electronically every Interactive Data File required to be submitted pursuant to Rule 405 of Regulation S-T (§232.405 of this chapter) during the preceding 12 months (or for such shorter period that the registrant was required to submit such files). Yes ☒ No ☐
Indicate by check mark whether the registrant is a large accelerated filer, an accelerated filer, a non-accelerated filer, a smaller reporting company, or an emerging growth company. See the definitions of “large accelerated filer,” “accelerated filer,” “smaller reporting company,” and “emerging growth company” in Rule 12b-2 of the Exchange Act.
| Large accelerated filer | ☒ | Accelerated filer | ☐ | ||||||||||||||
| Non-accelerated filer | ☐ | Smaller reporting company | ☐ | ||||||||||||||
| Emerging growth company | ☐ |
If an emerging growth company, indicate by check mark if the registrant has elected not to use the extended transition period for complying with any new or revised financial accounting standards provided pursuant to Section 13(a) of the Exchange Act. ☐
Indicate by check mark whether the registrant has filed a report on and attestation to its management’s assessment of the effectiveness of its internal control over financial reporting under Section 404(b) of the Sarbanes-Oxley Act (15 U.S.C. 7262(b)) by the registered public accounting firm that prepared or issued its audit report. ☒
Indicate by check mark whether the registrant is a shell company (as defined in Rule 12b-2 of the Act). Yes ☐ No ☒
The aggregate market value of voting stock held by non-affiliates of the registrant, as of June 30, 2021, the last business day of the registrant’s most recently completed second quarter, was $25,503,578,291 (based on the closing price for shares of the registrant’s common stock as reported by The Nasdaq Global Select Market on that date). Shares of common stock held by each executive officer, director, and holder of 5% or more of the registrant’s outstanding common stock have been excluded in that such persons may be deemed to be affiliates. This determination of affiliate status is not necessarily a conclusive determination for other purposes.
As of February 18, 2022, there were 160,815,446 shares of the registrant’s common stock outstanding.
DOCUMENTS INCORPORATED BY REFERENCE
Portions of the registrant’s definitive Proxy Statement relating to its 2022 Annual Meeting of Stockholders (“Proxy Statement”) are incorporated by reference into Part III of this Annual Report on Form 10-K where indicated. Such Proxy Statement will be filed with the United States Securities and Exchange Commission within 120 days after the end of the fiscal year to which this report relates.
FORTINET, INC.
ANNUAL REPORT ON FORM 10-K
For the Year Ended December 31, 2021
Table of Contents
Summary of Risk Factors
Our business is subject to numerous risks and uncertainties, including those described in Part I, Item 1A, “Risk Factors” in this Annual Report on Form 10-K. You should carefully consider these risks and uncertainties when investing in our common stock. Some of the principle risks and uncertainties include the following:
-
Our operating results are likely to vary significantly and be unpredictable.
-
The COVID-19 pandemic, including its ongoing variants, could adversely affect our business in a material way, based on, for example, component shortages or negative impact on demand.
-
Adverse economic conditions or reduced information technology spending may adversely impact our business.
-
Our billings, revenue, and free cash flow growth may slow or may not continue, and our operating margins may decline.
-
We are dependent on the continued services and performance of our senior management, as well as our ability to hire, retain and motivate qualified personnel, particularly for our sales organization.
-
We rely on third-party channel partners for substantially all of our revenue and a small number of distributors represents a large percentage of our revenue and accounts receivable.
-
Reliance on a concentration of shipments at the end of the quarter could cause our billings and revenue to fall below expected levels.
-
We rely significantly on revenue from FortiGuard security subscription and FortiCare technical support services, and revenue from these services may decline or fluctuate.
-
We have incurred indebtedness and may incur other debt in the future, which may adversely affect our financial condition and future financial results.
-
We generate a majority of revenue and cash flow from sales outside of the United States.
-
We may not be successful in executing our strategy to increase our sales to large- and medium-sized end-customers.
-
A portion of our revenue is generated by sales to government organizations, which are subject to a number of challenges and risks.
-
We face intense competition in our market and we may not maintain or improve our competitive position.
-
Insufficient inventory or components, including finished goods, chips and other components, and including component or inventory shortages related to the COVID-19 pandemic, manufacturer’s capacity, shipping challenges, or other factors affecting the global supply chain, may result in lost sales opportunities or delayed billings and revenue and increased costs, and may harm our gross margins and our product price increases designed to help mitigate lower gross margins may not be acceptable to customers.
-
We depend on third-party manufacturers to provide components for our products and build our products and are susceptible to manufacturing delays and cost increases.
-
We are susceptible to supply chain constraints, supply shortages and disruptions, long lead times for components and finished goods and supply changes because some of the key components in our products come from limited sources of supply.
-
We are susceptible to defects or vulnerabilities in our products or services, as well as reputational harm from the failure or misuse of our products or services.
-
Our proprietary rights may be difficult to enforce and we may be subject to claims by others that we infringe their proprietary technology.
-
The trading price of our common stock may be volatile, which volatility may be exacerbated by share repurchases under our Share Repurchase Program (the “Repurchase Program”).
-
Anti-takeover provisions contained in our certificate of incorporation and bylaws, as well as provisions of Delaware law, could impair a takeover attempt.
-
Global economic uncertainty and weakening product demand caused by political instability, changes in trade agreements and conflicts, such as the conflict between Russia and Ukraine, could adversely affect our business and financial performance.
Part I
Item 1. Business
Overview
Fortinet is a global leader in cybersecurity and networking solutions for organizations, including enterprises, communication service providers, security service providers, government organizations and small businesses.
The focus areas of our business consist of:
-
Convergence / Security-Driven Networking**—Our Security-Driven Networking solutions enable the convergence of networking and security across all edges to provide next-generation firewall (“NGFW”), software-defined wide area network (“SD-WAN”), LAN Edge (Wi-Fi and switch) and secure access service edge (“SASE”). Traditional networking lacks awareness of content, applications, users, devices, location and more. A security-driven networking approach converges networking and security into a single, accelerated solution. A specially designed operating system and security processors work in concert to greatly improve network performance and security posture while decreasing footprint and power consumption. We derive a majority of product sales from our FortiGate network security appliances. FortiGate network security appliances include a broad set of built-in security and networking features and functionalities, including firewall, next-generation firewall, secure web gateway, secure sockets layer (“SSL”) inspection, software-defined wide area network (“SD-WAN”), intrusion prevention system (“IPS”), sandboxing, data leak prevention, virtual private network (“VPN”), switch and wireless controller and wide area network (“WAN”) edge. Our network security appliances are managed by our FortiOS network operating system, which provides the foundation for FortiGate security functions. We enhance the performance of our network security appliances from branch to data center by designing and implementing security processing units (“SPUs”) technology within our appliances, enabling us to add security and network functionality with minimal impact to network throughput performance. Along with our secure Wi-Fi access points and switches, Fortinet helps organizations secure their networks across campuses, branches and work from anywhere (“WFA”) deployments.
-
Zero Trust Access**—Our Zero Trust Access solutions enable customers to know and control who and what is on their network, in addition to providing security for WFA. Zero Trust Access solutions include FortiNAC, FortiAuthenticator, FortiClient/EDR and FortiToken. Our network access control solutions provide visibility, control and automated event responses in order to secure internet of things (“IoT”) and operational technology (“OT”) devices.
-
Adaptive Cloud Security**—We help customers connect securely to and across their individual, hybrid cloud, multi-cloud and virtualized data center environments by offering security through our virtual firewall and other software products and through integrated capabilities with major cloud platforms. Our public and private cloud security solutions, including virtual appliances and hosted solutions, extend the core capabilities of the Fortinet Security Fabric cybersecurity mesh platform in and across cloud environments, delivering security that follows their applications and data. Our Secure SD-WAN for multi-cloud solution automates deployment of an overlay network across different cloud networks and offers visibility, control and centralized management that integrates functionality across multiple cloud environments. Our cloud security portfolio also includes securing applications, including email and web. Fortinet cloud security offerings are available for deployment in major public and private cloud environments, including Alibaba Cloud, Amazon Web Services, Google Cloud, IBM Cloud, Microsoft Azure, Oracle Cloud and VMWare Cloud. We also offer managed IPS and web application firewall (“WAF”) rules delivered by FortiGuard Labs as an overlay service to native security offerings offered by Amazon Web Services.
-
AI-Driven Security Operations**—We develop and provide a range of products and services that enable the security operations center (“SOC”) teams to identify, investigate and remediate potential incidents in which cybercriminals bypass prevention-oriented controls. Given the breadth of the attack surface to monitor, as well as the volume and sophistication of cyber threats, artificial intelligence (“AI”) is a key part of these offerings, which include: FortiGuard and other security subscription services, endpoint security with endpoint detection and response (“EDR”), a range of breach-protection technologies plus our security information and event management (“SIEM”) and security orchestration, automation and response (“SOAR”), all of which can be applied across the Fortinet Security Fabric cybersecurity mesh platform. These solutions automatically deliver security intelligence and insights that help organizations to protect against and respond to threats through integration with Fortinet and third-party solutions.
-
Security as a Service**—Our customers purchase our FortiGuard security subscription services as an add-on to products and solutions across the Fortinet Security Fabric to receive threat intelligence and protection updates. FortiGuard services are designed to provide protection for users and applications, including offerings for IPS, web, video and domain name system (“DNS”) filtering, audio/visual (“AV”) and cloud sandbox along with IoT and OT Security. The
FortiGuard security services are provided from our FortiGuard Labs and cloud-delivered to provide real-time unified protection across network endpoint and cloud.
- Support and Professional Services**—Fortinet offers technical support, FortiOS updates, and extended product warranty through our FortiCare support services. In addition to our technical support services, we offer a range of advanced services, including premium support, professional services and expedited warranty replacement. Our professional service offerings include resident engineers and professional service consultants for implementations or trainings.
During our year ended December 31, 2021, we generated total revenue of $3.34 billion and net income of $606.8 million. See Part II, Item 8 of this Annual Report on Form 10-K for more information on our consolidated balance sheets as of December 31, 2021 and 2020 and our consolidated statements of income, comprehensive income, equity, and cash flows for each of the three years ended December 31, 2021, 2020 and 2019.
We were incorporated in Delaware in November 2000. Our principal executive office is located at 899 Kifer Road, Sunnyvale, California 94086 and our telephone number at that location is (408) 235-7700.
Consolidation of Technology and Architecture
Cybersecurity has traditionally been deployed one solution at a time and not designed to work well with other deployed solutions while also increasing management complexity. A Fortinet Security Fabric cybersecurity mesh platform approach consolidates point products into a platform, allowing for much tighter integration, increased automation and a more rapid, coordinated, and effective response to threats across the network. The Fortinet Security Fabric has an open architecture designed to integrate Fortinet solutions and third-party solutions.
Our product offerings consist of our FortiGate network security products and our non-FortiGate products, which are offered in a broad range of form factors spanning physical appliances, virtual appliances, software and cloud-hosted services. This enables Fortinet to protect customers across all edges and deployment scenarios including users, devices, networks, cloud, and virtual data center. Our cloud- and hosted- products and services include sandboxing, endpoint detection and response (“EDR”), email security, web application and API security, and cloud networking security as well as Fortinet Security Fabric management and analytics. Additionally, we offer cloud-delivered and hosted-security services. Our FortiGuard security services are enabled by FortiGuard Labs, which provides threat research and artificial intelligence capabilities from a cloud network to deliver protection through FortiGate appliance and virtual machine as well as Fortinet Security Fabric products that are registered by the end-customer. All these are combined to form the Fortinet Security Fabric cybersecurity mesh platform, which is an approach to security that consolidates discrete security solutions together into an integrated offering. This integrated approach to security extends across both Fortinet developed solutions and a broad ecosystem of technology partner solutions and technologies.
SPU
Our proprietary SPUs are application-specific integrated circuits (“ASICs”) that include (i) the content processor (“SPU CP”), (ii) the network processor (“SPU NP”) and (iii) the system-on-a-chip (“SPU SoC”). Our SPUs are embedded in our physical FortiGate appliances and are designed to enhance the security processing capabilities of our operating system by accelerating computationally intensive tasks such as firewall policy enforcement, SD-WAN, network address translation, IPS, threat detection and encryption while also converging security capabilities with networking functionality. We also provide virtualized security processing units (“vSPUs”) across our FortiGate virtual appliances.
The use of SPUs allows our appliances to consolidate security functionality and converge security with a minimal impact to network throughput performance, which we believe delivers a lower total cost of ownership (“TCO”) to our customers. As the security needs and technologies of our end-customers increase, we believe our TCO-driven SPU approach give our products a competitive advantage against other architectural approaches.
Entry-level FortiGate products often use the SPU SoC to provide the necessary acceleration at this level. Mid-range FortiGate products use a central processing unit (“CPU”) and include the SPU NP and SPU CP hardware acceleration. The high-end FortiGate products use multiple CPUs, SPU CPs and SPU NPs.
FortiOS
FortiOS, its associated security and networking functions and products that run or are integrated with FortiOS are combined to form the Fortinet Security Fabric cybersecurity mesh platform. This approach to security ties discrete security solutions together into an integrated offering.
Our proprietary FortiOS operating system provides the foundation for the operation of FortiGate network security appliances, whether physical, virtual, private- or public-cloud based. We make regular enhancements and other updates to FortiOS available through our FortiCare support services.
The convergence of security and networking capabilities provided by the Fortinet Security Fabric cybersecurity mesh platform are powered and controlled through FortiOS. FortiOS provides (i) multiple layers of security, including a hardened kernel layer providing protection for the FortiGate system, (ii) a network security layer, providing security for end-customers’ network infrastructures and (iii) application content protection, providing security for end-customers’ workstations and applications. FortiOS directs the operations of processors and SPUs and provides system management functions such as command line, graphical user interfaces, multiple network and security topology views.
FortiOS also enables advanced, integrated routing and switching, allowing end-customers to deploy FortiGate devices within a wide variety of networks, as well as providing a direct replacement solution option for legacy switching and routing equipment. FortiOS implements a suite of commonly used standards-based routing protocols as well as network address translation technologies, allowing the FortiGate appliance to integrate and operate in a wide variety of network environments. Additional features include virtual domain capabilities, which can provide support for multiple customers on a single device or FortiOS instance in support of service provider and managed security service provider (“MSSP”) deployments. FortiOS also provides capabilities for the logging of traffic for forensic analysis purposes. FortiOS is designed to help control network traffic in order to optimize performance by including functionality such as packet classification, queue disciplines, policy enforcement, congestion management, WAN optimization and caching.
Products
Our core product offerings consist of our FortiGate firewall product family and our non-FortiGate products which may be purchased to integrate and expand security architectures. Our non-FortiGate products include the Fortinet Security Fabric cybersecurity mesh platform, email security, cloud security, endpoint protection and other products. Our FortiGate hardware and software licenses are sold with a set of FortiGate broad security services. These security services are enabled by FortiGuard Labs, which provides threat research and artificial intelligence capabilities from a global cloud network to deliver protection services.
FortiGate
FortiGate converges a broad set of security and networking functions, including firewall, intrusion prevention, anti-malware, VPN, application control, web filtering, anti-spam and WAN acceleration. FortiGate is available as a hardware appliance or as a virtual appliance. All FortiGate appliances run on FortiOS. FortiGate platforms can be centrally managed through both embedded web-based and command line interfaces, as well as through FortiManager, which provides a central management architecture for FortiGate appliances and the Fortinet Security Fabric cybersecurity mesh platform.
With over 35 models in the FortiGate product line, FortiGate is designed to address security requirements for small- to medium-sized businesses, large enterprises and government organizations worldwide.
Most FortiGate hardware appliances include one of our SPUs to accelerate content and network security features implemented within FortiOS. The significant differences between each model are the performance and scalability targets each model is designed to meet, while the security features and associated services offered are common throughout all models. The FortiGate-20 through -90 series models are designed for perimeter protection for small- to medium-sized businesses and enterprises with distributed offices. The FortiGate-100 through -900 series models are designed for perimeter deployment in medium-sized to large enterprise networks. The FortiGate-1000 through -7000 series models deliver high performance and scalable network security functionality for perimeter, data center and hyper scale data centers, and core deployment in large enterprises. In addition to networking security features, all FortiGate models and form factors also deliver secure SD-WAN capabilities. Fortinet also offers FortiGate Rugged models for OT applications where ruggedized appliances are needed.
We also incorporate additional technologies within FortiGate appliances that differentiate our solutions, including data leak protection, traffic optimization, SSL inspection, threat vulnerability management and wireless controller technology. In addition to these in-built features, we offer a full range of wireless access points and controllers, complementing FortiGate appliances with the flexibility of wireless local area network access.
Fortinet Security Fabric Cybersecurity Mesh Platform and Non-FortiGate Products
As part of the Fortinet Security Fabric cybersecurity mesh platform, we offer products that provide network security, endpoint security, cloud security, web-based application security, identity and access management, sandbox protection and
email security. The integration of devices using open standards, common operating systems, and unified management platforms enables the sharing and correlation of real-time threat intelligence. The following Fortinet products can operate as part of the Fortinet Security Fabric cybersecurity mesh platform:
- FortiAnalyzer**—Our FortiAnalyzer family of products provides centralized network logging, analyzing and reporting solutions that securely aggregate content and log data from our FortiGate devices, other Fortinet products and third-party devices to enable network logging, analysis and reporting.
*•*FortiAP—Our FortiAP product family provides secure wireless networking solutions. FortiAPs allow a variety of management options including from the cloud and directly from our FortiGate firewall product. FortiAPs create a scalable and secure access layer for connecting wireless devices such as computers, laptops, cell phones and tablets, as well as IoT devices.
-
FortiClient—Our FortiClient provides advanced endpoint protection with pattern-based anti-malware, behavior-based exploit protection, web-filtering and an application firewall. FortiClient integrates with FortiSandbox to detect zero-day threats and custom malware. FortiClient also provides secure remote access with built-in VPN, single-sign-on and two-factor authentication for added security.
-
FortiEDR/XDR—Our FortiEDR/XDR is an endpoint protection solution that provides both machine-learning anti-malware protection and remediation. FortiEDR/XDR supports broad OS coverage workstations, servers, and virtual machines, including legacy operating and embedded systems.
-
FortiGate-VM**— FortiGate-VM extends the Fortinet Security Fabric through the cloud on-ramp into the cloud, enabling customers to achieve security-driven networking within the cloud and between clouds and hybrid clouds. FortiGate-VM is powered by Fortinet vSPUs to deliver accelerated security and performance with minimal impact to performance. Our cloud networking solution enables better, more secure application experiences for users and branch offices by providing for encrypted data transports, granular segmentation and application-layer protection against advanced threats, and seamless overlay network with uniform policies across multi-clouds. FortiGate-VM is available for all major cloud providers, hypervisors and software-defined network (“SDN”) platforms.
-
FortiMail**—Our FortiMail product family provides secure email gateway solutions. FortiMail utilizes the technologies and security services from FortiGuard Labs to deliver protection against threats that use email as an attack vector. FortiMail also integrates data protection capabilities to avoid data loss.
-
FortiManager**—Our FortiManager family of products provides a central and scalable management solution for our FortiGate products, including software updates, configuration, policy settings and security updates. FortiManager facilitates the coordination of policy-based provisioning, device configuration and operating system revision management, as well as network security monitoring and device control.
-
FortiSandbox**—Our FortiSandbox technology delivers proactive detection and mitigation with the ability to generate a directly actionable protection capability. Available in both hardware and cloud-based form, the FortiSandbox subjects suspicious code to a set of multi-layer protection techniques, culminating in execution within an operating system, allowing real-time behavioral analysis to be performed in a secure environment. When malicious code is identified, a signature can be generated locally for distribution across the Fortinet Security Fabric cybersecurity mesh platform.
*•*FortiSwitch—Our FortiSwitch product family provides secure switching solutions that can be deployed in traditional network switching designs with Layer 2 or Layer 3 access control features. FortiSwitch creates a scalable and secure access layer for customers to connect their end devices, such as computers and laptops, as well as to expand the field of IoT devices.
*•*FortiToken—Our FortiToken allows organizations to implement two-factor authentication to better safeguard systems, assets and data. With two-factor authentication, a password is used along with a security token and authentication server to provide seamless yet highly secured access between users and applications. Authorized employees can access company resources safely using a variety of devices, ranging from laptops to mobile phones.
- FortiWeb—Our FortiWeb product family provides web application firewall solutions, including internet protocol (“IP”) reputation and anti-botnet security, distributed denial-of-service protection, protocol validation, application attack signatures and deep learning AI to protect applications against a wide range of threats.
The products listed above are available in multiple form factors, such as hardware, virtual machine, cloud or software-as-a-service (“SaaS”), except for FortiSwitch, FortiAP and FortiExtender, which are available as hardware appliances only and FortiGate-VM and FortiEDR/XDR which are available as virtual solutions only.
In the third quarter of 2021, we closed an acquisition of 75% of equity interests in Alaxala Networks Corporation (“Alaxala”), a privately held network hardware equipment company in Japan, to help address the increasing need for secure switches integrated with FortiGate firewalls and Security Fabric functionality, and, over time, to innovate and rebrand certain of Alaxala’s switches to offer a broader suite of secure switches globally. In the first quarter of 2021, we acquired ShieldX Networks Inc. (“ShieldX”), a provider of a security platform focusing on protecting multi-cloud data centers from the risk of lateral movement that can lead to attacks such as ransomware, data loss and service disruption.
Services
FortiGuard Security Subscription Services
Security requirements are dynamic due to the constantly changing nature of threats. Our FortiGuard security subscription services are designed to deliver threat detection and prevention capabilities to end-customers worldwide as threats evolve. Our FortiGuard Labs global threat research team identifies emerging threats, collects threat samples, and replicates, reviews, characterizes and collates attack data through the use of AI, automation and original research. Based on this research, we develop updates for virus signatures, attack definitions, scanning engines and other security solution components to distribute to end-customers. FortiGuard functionality varies depending on the FortiGate and non-FortiGate products, and will typically include one or more of the following functions: application control, antivirus, intrusion prevention, web filtering, anti-spam, VPN functions, email image analysis, vulnerability management, database functions, web functions, advanced threat protection, sandboxing and domain and IP reputation services.
End-customers purchase FortiGuard security subscription services in advance, typically with terms of one to five years. We provide FortiGuard security subscription services 24 hours a day, seven days a week.
FortiCare Technical Support Services
Our FortiCare support services portfolio includes technical support, FortiOS updates and extended product warranty. For our standard technical support, our channel partners may provide first-level support to the end-customer. We also provide first-level support to our end-customers, as well as second- and third-level support as appropriate. We also provide knowledge management tools and customer self-help portals to help augment our support capabilities in an efficient and scalable manner. We deliver technical support to partners and end-customers 24 hours a day, seven days a week, through regional technical support centers. In addition to our technical support services, we offer a range of advanced services, including premium support, professional services and expedited warranty replacement.
Service Bundles
We also sell FortiGuard and FortiCare services as bundles, consolidating security services into packages that are appropriate for different use cases or end-customers.
-
Advanced Threat Protection**—Our Advanced Threat Protection bundle includes antivirus, data sanitation sandbox, intrusion prevention, virus outbreak protection, mobile security, application control, IP reputation and anti-botnet security, along with FortiCare support services.
-
Unified Threat Protection**—Our Unified Threat Protection bundle includes the Advanced Threat Protection security services noted above, as well as intrusion prevention, virus outbreak protection, web filtering and FortiCare support services.
-
Enterprise Protection**—Our Enterprise Protection bundle includes the Unified Threat Protection services noted above, as well as industrial control systems, security rating, along with enhanced FortiCare support services.
-
Small Medium Business –** Our Small Medium Business bundle includes the Unified Threat Protection services noted above, as well as FortiGate Cloud which provides cloud-based management, reporting, and analytics for FortiGates along with enhanced FortiCare support services.
Professional Services
We offer professional services to end-customers including technical account managers (“TAMs”), resident engineers (“REs”) and professional service consultants, security architects for implementations and remote, cloud-based incident response (“IR”).
TAMs and REs are dedicated support engineers available to help identify and eliminate issues before problems arise. Each TAM and RE acts as a single point of contact and customer advocate within Fortinet, offering a deep understanding of our customers’ businesses and security requirements.
Our professional services consultants and security architects help to formulate customer-specific security strategies, develop roadmaps for securing digital initiatives and design product deployments. They work closely with end-customers to implement our products according to design, utilizing network analysis tools, traffic simulation software and scripts.
Fortinet also offers remote, cloud-based IR and monitoring services to help customers identify, remediate and understand compromises. This service leverages our FortiEDR capabilities either as part of a premium FortiEDR subscription for continuous monitoring or alternatively, can be deployed to help deliver IR services on a per incident basis.
Training Services
We offer training services to our end-customers and channel partners through our training team and authorized training partners. We have also implemented a training certification program, Network Security Expert, to help ensure an understanding of our products and services. Since 2020, Fortinet also offers a number of free online training courses to help address prevalent industry-wide cybersecurity skills gaps and shortages.
Customers
We typically sell our security solutions to distributors that sell to networking security focused resellers and to service providers and managed security service providers (“MSSPs”), who, in turn, sell products and/or services to end-customers. At times, we also sell directly to large service providers and major systems integrators who may sell to our end-customers or use our products and services to provide hosted solutions to other enterprises. Our end-customers are located in over 100 countries and include small, medium and large enterprises and government organizations across a wide range of industries, including telecommunications, government, financial services, retail, technology, education, manufacturing and healthcare. An end-customer deployment may involve as few as one or as many as thousands of appliances as well as other Fortinet Security Fabric cybersecurity mesh platform products. Customers may also access our products via the cloud through certain cloud providers such as Alibaba Cloud, Amazon Web Services, Google Cloud, IBM Cloud, Microsoft Azure and Oracle Cloud. Often, our customers also purchase our FortiGuard security subscription services and FortiCare technical support services.
During 2021, Exclusive Networks Group (“Exclusive”) and Ingram Micro Inc. (“Ingram Micro”) accounted for 31% and 12% of total revenue, respectively. During 2020, Exclusive and Ingram Micro accounted for 30% and 10% of total revenue, respectively. During 2019, Exclusive and Ingram Micro accounted for 31% and 11% of total revenue, respectively.
Sales and Marketing
We primarily sell our products and services through a two-tier distribution model. We sell to distributors that sell to resellers and to service providers and MSSPs, who, in turn, sell products and/or services to end-customers. In certain cases, we sell directly to large service providers and major systems integrators. We work with many technology distributors, including Arrow Electronics, Inc., Exclusive, Ingram Micro and TD Synnex (formerly Tech Data Corporation and Synnex Corporation, separately).
We support our channel partners with a dedicated team of experienced channel account managers, sales professionals and sales engineers who provide business planning, joint marketing strategy, pre-sales and operational sales support. Additionally, our sales teams help drive and support large enterprise and service provider sales through a direct touch model. Our sales professionals and engineers typically work closely with our channel partners and directly engage with large end-customers to address their unique security and deployment requirements. To support our broadly dispersed global channel and end-customer base, we have sales professionals in over 100 countries around the world.
Our marketing strategy is focused on building our brand, driving thought leadership with emphasis on the criticality of cybersecurity platform adoption and the convergence of security and networking as well as driving end-customer demand for our security solutions. We use a combination of internal marketing professionals and a network of regional and global channel partners. Our internal marketing organization is responsible for messaging, branding, demand generation, product marketing, channel marketing, partner incentives and promotions, event marketing, digital marketing, communications, analyst relations, public relations and sales enablement. We focus our resources on campaigns, programs and activities that can be leveraged by partners worldwide to extend our marketing reach, such as sales tools and collateral, product awards and technical certifications, media engagement, training, regional seminars and conferences, webinars and various other demand-generation activities.
In 2021, we continued to invest in sales and marketing resources, particularly in the enterprise market where we believe there is an opportunity to expand our business. We intend to continue to make investments in sales and marketing resources, which are critical to support our growth.
Manufacturing and Suppliers
We outsource the manufacturing of our security appliance products to a variety of contract manufacturers and original design manufacturers. Our current manufacturing partners include ADLINK Technology, Inc. (“ADLINK”), IBASE Technology, Inc. (“IBASE”), Micro-Star International Co. (“Micro-Star”), Senao Networks, Inc. (“Senao”), Wistron Corporation (“Wistron”) and a number of other manufacturers. Approximately 83% of our hardware is manufactured in Taiwan. We submit purchase orders to our contract manufacturers that describe the type and quantities of our products to be manufactured, the delivery date and other delivery terms. Once our products are manufactured, they are sent to either our warehouse in California or to our logistics partner in Taoyuan City, Taiwan, where accessory packaging and quality-control testing are performed. We believe that outsourcing our manufacturing and a substantial portion of our logistics enables us to focus resources on our core competencies. Our proprietary SPUs, which are key to the performance of our appliances, are built by contract manufacturers including Toshiba America Electronic Components, Inc. (“Toshiba”) and Renesas Electronics America, Inc. (“Renesas”). These contract manufacturers use foundries in Taiwan and Japan operated by either Taiwan Semiconductor Manufacturing Company Limited (“TSMC”) or by the contract manufacturer itself.
The components included in our products are sourced from various suppliers by us or, more frequently, by our contract manufacturers. Some of the components important to our business, including certain CPUs from Intel Corporation (“Intel”), network chips from Broadcom Inc. (“Broadcom”), Marvell Technology Group Ltd. (“Marvell”) and Intel, and memory devices from Intel, ADATA Technology Co., Ltd. (“ADATA”), OCZ Technology Group, Inc., Samsung Electronics Co., Ltd. (“Samsung”), and Western Digital Technologies, Inc. (“Western Digital”), are available from limited or sole sources of supply.
We have no long-term contracts related to the manufacturing of our ASICs or other components that guarantee any capacity or pricing terms.
Research and Development
We focus our research and development efforts on developing new hardware and software products and services, and adding new features to existing products and services. Our development strategy is to identify features, products and systems for both software and hardware that are, or are expected to be, important to our end-customers. Our success in designing, developing, manufacturing and selling new or enhanced products will depend on a variety of factors, including identification of market demand for new products or new features, components selection, timely implementation of product design and development, product performance, quality, ease of use, costs of development, bill of materials, effective manufacturing and assembly processes and sales and marketing.
Intellectual Property
We rely primarily on patent, trademark, copyright and trade secrets laws, confidentiality procedures and contractual provisions to protect our technology. We periodically have discussions with third parties regarding licensing Fortinet’s intellectual property (“IP”) and have sometimes taken legal action against competitors to protect our IP, and as a result third parties have paid us fees in return for licenses or covenants-not-to-sue related to Fortinet IP. As of December 31, 2021, we had 1,255 U.S. and foreign-issued patents and 254 pending U.S. and foreign patent applications. We also license software from third parties for inclusion in our products, including open source software and other software.
Despite our efforts to protect our rights in our technology, unauthorized parties may attempt to copy aspects of our products or obtain and use information and technology that we regard as proprietary. We generally enter into confidentiality agreements with our employees, consultants, vendors and customers, and generally limit access to and distribution of our
proprietary information. However, we cannot provide assurance that the steps we take will prevent misappropriation of our technology. In addition, the laws of some foreign countries do not protect our proprietary rights to as great an extent as the laws of the United States, and many foreign countries do not enforce these laws as diligently as government agencies and private parties in the United States.
Our industry is characterized by the existence of a large number of patents and frequent claims and related litigation regarding patent and other IP rights. Third parties have asserted, are currently asserting and may in the future assert patent, copyright, trademark or other IP rights against us, our channel partners or our end-customers. Successful claims of infringement by a third-party could prevent us from distributing certain products or performing certain services or require us to pay substantial damages (including treble damages if we are found to have willfully infringed patents or copyrights), royalties or other fees. Even if third parties offer a license to their technology, the terms of any offered license may not be acceptable and the failure to obtain a license or the costs associated with any license could cause our business, operating results or financial condition to be materially and adversely affected. In certain instances, we indemnify our end-customers, distributors and resellers against claims that our products infringe the IP of third parties.
Government Regulation
We are subject to regulation by various federal, state, regional, local and foreign governmental agencies, including agencies responsible for monitoring and enforcing employment and labor laws, workplace safety, product safety, product labeling, environmental laws, consumer protection laws, anti-bribery laws, data privacy laws, import and export controls, federal securities laws and tax laws and regulations. Many of the laws and regulations that are or may be applicable to our business are changing or being tested in courts and could be interpreted in ways that could adversely impact our business. In addition, the application and interpretation of these laws and regulations often are uncertain, particularly in the industry in which we operate. We believe we are in compliance with current laws and regulations and do not expect continued compliance to have a material impact on our capital expenditures, earnings, or competitive position. We continue to monitor existing and pending laws and regulations and while the impact of regulatory changes cannot be predicted with certainty, we do not currently expect compliance to have a material adverse effect.
Seasonality
For information regarding seasonality in our sales, see the section entitled “Management’s Discussion and Analysis of Financial Condition and Results of Operations—Seasonality, Cyclicality and Quarterly Revenue Trends” in Part II, Item 7 of this Annual Report on Form 10-K.
Competition
The markets for our products are extremely competitive and are characterized by rapid technological change. The principal competitive factors in our markets include the following:
-
product security performance, throughput, features, effectiveness, interoperability and reliability;
-
addition and integration of new networking and security features and technological expertise;
-
compliance with industry standards and certifications;
-
price of products and services and total cost of ownership;
-
brand recognition;
-
customer service and support across varied and complex customer segments and use cases;
-
sales and distribution capabilities;
-
size and financial stability;
-
breadth of product line;
-
form factor of the solution; and
-
other competitive differentiators.
Among others, our competitors include Barracuda Networks, Inc. (“Barracuda”), Check Point Software Technologies Ltd. (“Check Point”), Cisco Systems, Inc. (“Cisco”), CrowdStrike Holdings, Inc. (“CrowdStrike”), F5 Networks, Inc. (“F5 Networks”), Forcepoint LLC (“Forcepoint”), Imperva, Inc. (“Imperva”), Juniper Networks, Inc. (“Juniper”), Mandiant, Inc. (“Mandiant”), McAfee, LLC (“McAfee”), Palo Alto Networks, Inc. (“Palo Alto Networks”), Proofpoint, Inc. (“Proofpoint”), SonicWALL, Inc. (“SonicWALL”), Sophos Group Plc (“Sophos”), Trend Micro Incorporated (“Trend Micro”) and Zscaler, Inc. (“Zscaler”).
We believe we compete favorably based on our products’ security performance, throughput, reliability, breadth and ability to work together, our ability to add and integrate new networking and security features and our technological expertise. Several competitors are significantly larger, have greater financial, technical, marketing, distribution, customer support and other resources, are more established than we are, and have significantly better brand recognition. Some of these larger competitors have substantially broader product offerings and leverage their relationships based on other products or incorporate functionality into existing products in a manner that discourages users from purchasing our products. Based in part on these competitive pressures, we may lower prices or attempt to add incremental features and functionalities to our products.
Conditions in our markets could change rapidly and significantly as a result of technological advancements, market consolidation, supply chain constraints, price list or discount changes or inflation. The development and market acceptance of alternative technologies could decrease the demand for our products or render them obsolete. Our competitors may introduce products that are less costly, provide superior performance, are better marketed, or achieve greater market acceptance than our products. Additionally, our larger competitors often have broader product lines and are better positioned to withstand a significant reduction in capital spending by end-customers, and will therefore not be as susceptible to downturns in a particular market. The above competitive pressures are likely to continue to impact our business. We may not be able to compete successfully in the future, and competition may harm our business.
Human Capital Management
As of December 31, 2021, our total headcount was 10,195 employees, approximately 30% of whom were employed in the United States and approximately 70% of whom were employed outside of the United States.
Our employees are the foundation of our innovation and cybersecurity leadership for the benefit of our customers. We understand there is a shortage of highly skilled employees for security companies like ours, and we believe that our success and competitive advantage depends largely on our ability to continue to attract and retain highly skilled employees with diverse backgrounds and experiences. We believe we offer fair, competitive compensation and benefits, and we encourage a culture of fairness and meritocracy. Our compensation programs for our employees include base pay, incentive compensation, opportunities for equity ownership where local statutes allow and employee benefits that promote well-being across different aspects of our employees’ lives, which may include health and welfare insurance, retirement benefits and paid time off.
As a global company, much of our success is rooted in the diversity of our teams and our commitment to diversity, equity and inclusion. Such commitment starts at the top, with a highly skilled and diverse board of directors. As of December 31, 2021, women represented one-third of the members of our board of directors, and approximately 56% of our board of directors was from underrepresented communities as defined by California’s Assembly Bill 979. We value diversity at all levels and continue to focus on enhancing our diversity, equity and inclusion initiatives across our workforce.
We are also committed to community engagement and social responsibility with regards to our employees and beyond, and our board of directors has active oversight of such initiatives. Examples of our initiatives focused on our employees include our company matching program for employee charitable contributions and the free security training programs we offer to help with career development for our employees, in addition to the general public.
Our culture is defined by our commitment to ethics and integrity. We reinforce our ethical “tone at the top” through clear policies including our Code of Business Conduct and Ethics, regular compliance training for our employees, quarterly meetings of our cross-functional Ethics Committee, clear messaging from our executives, enforcement of company policies and oversight by our board of directors. In addition, our Chief Executive Officer regularly communicates the importance of Fortinet’s core values of openness, teamwork and innovation.
We are committed to providing our employees a safe and healthy work environment. We sponsor a global wellness program designed to enhance physical, financial and mental wellbeing for all our employees around the world. Throughout the year, we encourage healthy behaviors through communications, educational sessions, wellness challenges and other incentives.
Early in the COVID-19 pandemic, our Chief Executive Officer committed to having no COVID-related layoffs, and, throughout the pandemic, not only have we kept that promise, we have continued hiring at a fast pace and have continued to help support our employees and their families through this challenging time. During the pandemic, we have taken a flexible approach to help our employees manage their work and personal responsibilities, with a focus on employee wellbeing, health and safety.
None of our U.S. employees are represented by a labor union. Our employees in certain European and Latin American countries, however, have the right to be represented by external labor organizations if they maintain up-to-date union membership. We have not experienced any work stoppages, and we consider our relations with our employees to be good.
Environmental, Social and Governance
We are committed to responsible environmental, social and governance (“ESG”) practices. This commitment starts with the Social Responsibility Committee of our board of directors providing oversight of our Corporate Social Responsibility (“CSR”) strategy, initiatives and execution related to ESG matters. Our senior leadership sponsors the integration of CSR priorities throughout our business operations. In addition, our Global Head of Sustainability and CSR, along with our internal cross-functional employee CSR Committee, engage with internal and external stakeholders to lead CSR execution, communications and disclosure.
Environmental. We recognize climate change is a global crisis and are committed to doing our part to reduce negative environmental impact by setting clear goals, engaging in coalitions and collaborating across our value chain. We have engaged with a consultancy to measure our Scope 1 and Scope 2 emissions and developed reduction plans based on science-based targets pathways. We also have begun to conduct an inventory of our Scope 3 emissions to look at the decarbonization of our broader value chain. Those actions align with our roadmap on helping do our part to mitigate climate change, with the aim of implementing a framework that aligns with the Task Force on Climate Related Financial Disclosures (“TCFD”).
In November 2021, we publicly committed to a target of carbon neutrality on our Scope 1 and Scope 2 emissions by 2030 and announcing the completion of our new, net-zero building on our Sunnyvale headquarters campus, which was designed to be LEED-Gold certified.
Social. As discussed above, we prioritized the health and safety of our employees during the COVID-19 pandemic. Through our Global Supplier Code of Conduct and Contract Manufacturer agreement, we continued to reach across our supply chain to communicate our expectations regarding human rights, labor standards, business practices and workplace health and safety conditions. We are also committed to building an inclusive, equitable and diverse workforce within our organization and across the security industry, to help empower individuals to reach their full potential. In line with that commitment, we are focused on diversity, equity and inclusion as part of our mission to close the cybersecurity skills gap. Last year, we formalized our Education Outreach Program, which focuses on partnerships across the industry, academia, government and nonprofits to ensure we are helping train women, veterans and other under-represented groups. To support the creation of a cybersecurity-aware society, we published a children’s book designed to further increase cyber awareness among children and extended our free cybersecurity training courses empowering over 100,000 people from over 200 countries and territories to learn from our cyber-security training courses in 2021. We also made a public pledge to train one million people in cybersecurity by 2026.
Governance. Our culture is defined by our commitment to ethics and integrity. We stress the importance of ethical business practices in multiple ways, such as through our Code of Business Conduct and Ethics, regular compliance training programs and ongoing communications. Reinforcing the importance of our ESG contributions, our board of directors established its Social Responsibility Committee to oversee our objectives, strategy and execution relating to sustainability and CSR, including ESG matters. As part of our regular engagement with our stockholders and our commitment to ESG, including our regular review of our corporate governance structure and evaluation of recent trends in corporate governance, we have evolved our corporate governance practices over time and have, since becoming a public company, implemented the following measures, among others: majority voting standard for uncontested elections of directors, allowing stockholders to call special meetings of our stockholders, declassification of our board of directors, proxy access, and stock ownership guidelines with respect to our non-employee directors.
Available Information
Our web site is located at https://www.fortinet.com, and our investor relations web site is located at https://investor.fortinet.com. The information posted on our website is not incorporated by reference into this Annual Report on Form 10-K. Our Annual Report on Form 10-K, Quarterly Reports on Form 10-Q, Current Reports on Form 8-K and amendments to reports filed or furnished pursuant to Sections 13(a) and 15(d) of the Securities Act, are available free of charge on our investor relations web site as soon as reasonably practicable after we electronically file such material with, or furnish it to, the SEC. You may also access all of our public filings through the SEC’s website at https://www.sec.gov.
We webcast our earnings calls and certain events we participate in or host with members of the investment community on our investor relations web site. Additionally, we provide notifications of news or announcements regarding our financial performance, including SEC filings, investor events and press and earnings releases, as part of our investor relations web site. The contents of these web sites are not intended to be incorporated by reference into this report or in any other report or document we file.
Item 1A. Risk Factors
Investing in our common stock involves a high degree of risk. Investors should carefully consider the following risks and all other information contained in this Annual Report on Form 10-K, including our consolidated financial statements and the related notes, before investing in our common stock. The risks and uncertainties described below are not the only ones we face. Additional risks and uncertainties that we are unaware of, or that we currently believe are not material, also may become important factors that affect us. If any of the following risks materialize, our business, financial condition and results of operations could be materially harmed. In that case, the trading price of our common stock could decline substantially, and investors may lose some or all of their investment. We have summarized risks immediately below and encourage investors to carefully read the entirety of this Risk Factors section.
Risks Related to Our Business and Financial Position
Our operating results are likely to vary significantly and be unpredictable.
Our operating results have historically varied from period to period, and we expect that they will continue to do so as a result of a number of factors, many of which are outside of our control or may be difficult to predict, including:
-
our ability to attract and retain new end-customers or sell additional products and services to our existing end-customers;
-
component shortages, including chips and other components, and product inventory shortages, including those caused by factors outside of our control, such as the COVID-19 pandemic, supply chain disruptions, inflation and other cost increases, international trade disputes or tariffs, natural disasters, health emergencies, power outages, civil unrest, labor disruption, international conflicts, such as the conflict between Russia and Ukraine, terrorism, wars and critical infrastructure attacks;
-
inventory management;
-
the level of demand for our products and services, which may render forecasts inaccurate, increase backlog and may be impacted by the COVID-19 pandemic and supply chain constraints in ways that we are not able to foresee;
-
supplier cost increases and any lack of market acceptance of our price increases designed to help offset any supplier cost increases;
-
the timing of channel partner and end-customer orders, market acceptance of our price increases, and our reliance on a concentration of shipments at the end of each quarter;
-
the impact to our business, the global economy, disruption of global supply chains and creation of significant volatility and disruption of the financial markets due to the COVID-19 pandemic;
-
the timing of shipments, which may depend on factors such as inventory levels, logistics, manufacturing or shipping delays, our ability to ship products on schedule and our ability to accurately forecast inventory requirements and our suppliers ability to deliver components and finished goods;
-
increased expenses, unforeseen liabilities or write-downs and any negative impact on results of operations from any acquisition or equity investment consummated, as well as accounting risks, integration risks related to product plans and products and risks of negative impact by such acquisitions and equity investments on our financial results;
-
the mix of products sold, such as the mix between FortiGate and non-FortiGate solutions, and the mix of revenue between products and services, as well as the degree to which products and services are bundled and sold together for a package price;
-
the purchasing practices and budgeting cycles of our channel partners and end-customers, including the effect of the end of product lifecycles or refresh cycles;
-
any decreases in demand by channel partners or end-customers, including any such decreases caused by factors outside of our control such as natural disasters and health emergencies, including earthquakes,
droughts, fires, power outages, typhoons, floods, pandemics or epidemics such as the COVID-19 pandemic and manmade events such as civil unrest, labor disruption, international trade disputes, international conflicts, terrorism, wars and critical infrastructure attacks;
-
the effectiveness of our sales organization, generally or in a particular geographic region, the time it takes to hire sales personnel and the timing of hiring, and our ability to hire and retain effective sales personnel;
-
sales execution risk related to effectively selling to all segments of the market, including enterprise and small- and medium-sized businesses, government organizations and service providers, and to selling our broad security product and services portfolio, including, among other execution risks, risks associated with the complexity and distraction in selling to all segments and increased competition and unpredictability of timing to close larger enterprise and large organization deals;
-
execution risk associated with our efforts to capture the opportunities related to our identified growth drivers, such as risk associated with our ability to capitalize on the convergence of networking and security, vendor consolidation of various cyber security solutions, SD-WAN, infrastructure security, cloud security and endpoint protection, and IoT and OT security opportunities;
-
the seasonal buying patterns of our end-customers;
-
the timing and level of our investments in sales and marketing, and the impact of such investments on our operating expenses, operating margin and the productivity, capacity, tenure and effectiveness of execution of our sales and marketing teams;
-
the timing of revenue recognition for our sales, including any impacts resulting from extension of payment terms to distributors and backlog levels;
-
the level of perceived threats to network security, which may fluctuate from period to period;
-
any actual or perceived vulnerabilities in our products or services, and any actual or perceived breach of our network or our customers’ networks;
-
changes in the requirements, market needs or buying practices and patterns of our distributors, resellers or end-customers;
-
changes in the growth rates of the network security market in particular and other security and networking markets, such as SD-WAN, OT, switches, access points and cloud solutions for which we and our competitors sell products and services;
-
the timing and success of new product and service introductions or enhancements by us or our competitors, or any other change in the competitive landscape of our industry, including consolidation among our competitors, partners or end-customers;
-
the deferral of orders from distributors, resellers or end-customers in anticipation of new products or product enhancements announced by us or our competitors; or the acceleration of orders in response to our announced or expected price list increases;
-
increases or decreases in our billings, revenue and expenses caused by fluctuations in foreign currency exchange rates or a strengthening of the U.S. dollar, as a significant portion of our expenses is incurred and paid in currencies other than the U.S. dollar, and the impact such fluctuations may have on the actual prices that our partners and customers are willing to pay for our products and services;
-
compliance with existing laws and regulations;
-
our ability to obtain and maintain permits, clearances, and certifications that are applicable to our ability to conduct business with the public sector, including the U.S. federal government, and other sectors;
-
litigation, litigation fees and costs, settlements, judgments and other equitable and legal relief granted related to litigation;
-
the impact of cloud-based security solutions on our billings, revenues, operating margins and free cash flow;
-
decisions by potential end-customers to purchase network security solutions from newer technology providers, from larger, more established security vend
Showing the first 8K of 175K characters. Open the full section
Item 1B. Unresolved Staff Comments
Not applicable.
Item 2. Properties
Our corporate headquarters is located in Sunnyvale, California and comprises approximately 390,000 square feet of building space on twenty acres of land. Along with our corporate headquarters, as of December 31, 2021, we own approximately 290,000 square feet in Union City, California, used for manufacturing assembly and operations; approximately 460,000 square feet of office space in Burnaby and Ottawa, Canada, used for operations, support and research and development work; approximately 100,000 square feet of office space in Florida; approximately 90,000 square feet of office space in Texas; and approximately 70,000 square feet of office space in Valbonne, France, predominantly used for sales and support. We also own additional building space in Sunnyvale and Union City, California, for future development of approximately 140,000 square feet.
We maintain additional leased offices throughout the world, predominantly used as sales and support offices. We believe that our existing properties are sufficient and suitable to meet our current needs. We intend to expand our facilities or add new facilities to support our future growth and enter new geographic markets, and we believe that suitable additional or alternative space will be available or can be developed as needed to accommodate ongoing operations and any such growth.
However, we expect to incur additional operating expenses and capital expenditures in connection with such new or expanded facilities.
For information regarding the geographical location of our property and equipment, refer to Note 17 to our consolidated financial statements in Part II, Item 8 of this Annual Report on Form 10-K.
Item 3. Legal Proceedings
We are subject to various claims, complaints and legal actions that arise from time to time in the normal course of business. We accrue for contingencies when we believe that a loss is probable and that we can reasonably estimate the amount of any such loss. There can be no assurance that existing or future legal proceedings arising in the ordinary course of business or otherwise will not have a material adverse effect on our business, consolidated financial position, results of operations or cash flows.
In December 2021, we entered into an agreement that provided for settlement and dismissal of an existing patent infringement lawsuit and a mutual covenant-not-to-sue for a defined duration of time. Please refer to Note 13. Commitments and Contingencies in Part II, Item 8 of this Annual Report on Form 10-K for additional information.
Item 4. Mine Safety Disclosure
Not applicable.
Part II
Item 5. Market for Registrant’s Common Equity, Related Stockholder Matters and Issuer Purchases of Equity Securities
Common Stock
Our common stock is traded on The Nasdaq Global Select Market under the symbol “FTNT.”
Holders of Record
As of February 18, 2022, there were 43 holders of record of our common stock. A substantially greater number of holders of our common stock are “street name” or beneficial holders, whose shares are held by banks, brokers and other financial institutions.
Dividends
We have never declared or paid cash dividends on our capital stock. We do not anticipate paying any cash dividends in the foreseeable future. Any future determination to declare cash dividends will be made at the discretion of our board of directors and will depend on our financial condition, operating results, capital requirements, general business conditions and other factors that our board of directors may deem relevant.
Securities Authorized for Issuance Under Equity Compensation Plans
Information responsive to this item is incorporated herein by reference to our definitive proxy statement with respect to our 2022 Annual Meeting of Stockholders to be filed with the Securities and Exchange Commission (the “SEC”) within 120 days after the end of the fiscal year covered by this Annual Report on Form 10-K.
Stock Performance Graph
This performance graph shall not be deemed “filed” for purposes of Section 18 of the Securities and Exchange Act of 1934 (the “Exchange Act”), or incorporated by reference into any filing of Fortinet under the Securities Act of 1933, as amended (the “Securities Act”), or the Exchange Act, except as shall be expressly set forth by specific reference in such filing.
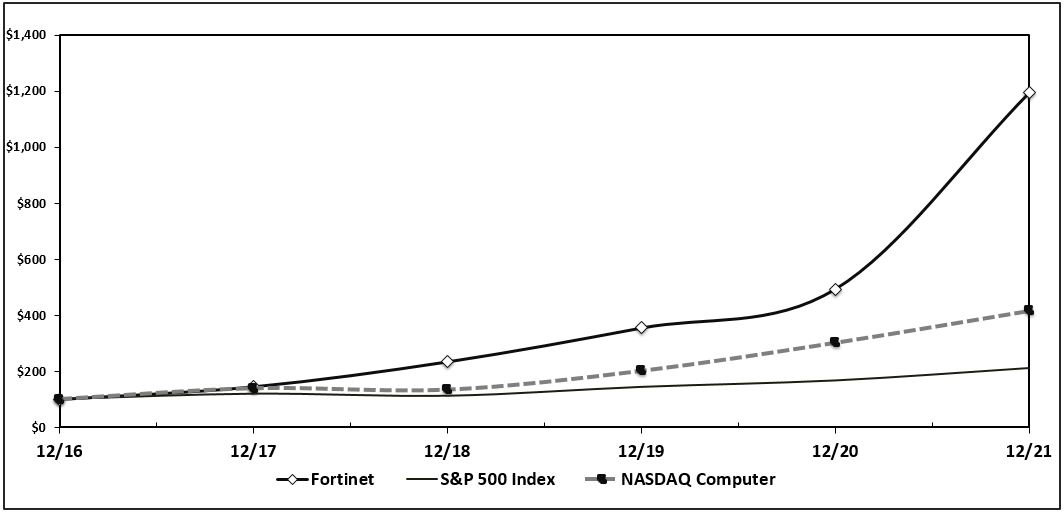
The following graph compares the cumulative five-year total return for our common stock, the Standard & Poor’s 500 Stock Index (the “S&P 500 Index”) and the NASDAQ Computer Index. Such returns are based on historical results and are not
intended to suggest future performance. Data for the S&P 500 Index and the NASDAQ Computer Index assume reinvestment of dividends.
COMPARISON OF CUMULATIVE TOTAL RETURN*
Among Fortinet, Inc., the S&P 500 Index and
the NASDAQ Computer Index
| **December 2016 *** | December 2017 | December 2018 | December 2019 | December 2020 | December 2021 | |||||||||||||||||||||||||||||||||
| Fortinet, Inc. | $ | 100 | $ | 145 | $ | 234 | $ | 354 | $ | 493 | $ | 1,193 | ||||||||||||||||||||||||||
| S&P 500 Index | $ | 100 | $ | 119 | $ | 112 | $ | 144 | $ | 168 | $ | 213 | ||||||||||||||||||||||||||
| NASDAQ Computer | $ | 100 | $ | 139 | $ | 134 | $ | 201 | $ | 301 | $ | 415 | ||||||||||||||||||||||||||
| * Assumes that $100 was invested on December 31, 2016 in stock or index, including reinvestment of dividends. Stockholder returns over the indicated period should not be considered indicative of future stockholder returns. |
Sales of Unregistered Securities
None.
Purchases of Equity Securities by the Issuer and Affiliated Purchasers
Share Repurchase Program
In January 2016, our board of directors approved our Share Repurchase Program (the “Repurchase Program”), which authorized the repurchase of up to $200.0 million of our outstanding common stock through December 31, 2017. From 2016 through 2020, our board of directors approved increases to our Repurchase Program by various amounts, bringing the aggregated amount authorized to $3.0 billion. In October 2021, our board of directors approved a $1.25 billion increase and extended the term to February 28, 2023, bringing the aggregate amount authorized to be repurchased to $4.25 billion. Under the Repurchase Program, share repurchases may be made by us from time to time in privately negotiated transactions or in open market transactions. The Repurchase Program does not require us to purchase a minimum number of shares, and may be suspended, modified or discontinued at any time without prior notice. Since its inception, we have repurchased 35.1 million shares of our common stock under the Repurchase Program for an aggregate purchase price of $2.73 billion.
The following table provides information with respect to the shares of common stock we repurchased during the three months ended December 31, 2021 (in millions, except per share amounts):
| Total Number of Shares Purchased | Average Price Paid per Share | Total Number of Shares Purchased as Part of Publicly Announced Plans or Programs | Approximate Dollar Value of Shares that May Yet Be Purchased Under the Plans or Programs | |||||||||||||||||||||||
| October 1 - October 31, 2021 | 0.2 | $ | 291.82 | 0.2 | $ | 2,005.4 | ||||||||||||||||||||
| November 1 - November 30, 2021 | 0.1 | 325.05 | 0.1 | 1,963.7 | ||||||||||||||||||||||
| December 1 - December 31, 2021 | 1.5 | 308.77 | 1.5 | 1,520.9 | ||||||||||||||||||||||
| Total | 1.8 | 1.8 |
Item 6. [Reserved]
Item 7. Management’s Discussion and Analysis of Financial Condition and Results of Operations
In addition to historical information, this Annual Report on Form 10-K contains forward-looking statements within the meaning of Section 27A of the Securities Act and Section 21E of the Exchange Act. These statements include, among other things, statements concerning our expectations regarding:
*•*the effects of supply chain constraints and the global chip and component shortages and other factors affecting our manufacturing capacity, delivery, cost and inventory management;
*•*the duration and impact of the COVID-19 pandemic, including various COVID-19 variants, and the implementation of “return to office” plans;
*•*continued growth and market share gains;
*•*variability in sales in certain product categories from year to year and between quarters;
*•*expected impact of sales of certain products and services;
*•*the impact of macro-economic, geopolitical factors and other disruption on our manufacturing or sales, including the impact of the COVID-19 pandemic and other public health issues and natural disasters;
-
the proportion of our revenue that consists of product and service revenue, and the mix of billings between products and services, and the duration of service contracts;
-
the impact of our product innovation strategy;
-
the effects of government regulation, tariffs and other policies;
-
drivers of long-term growth and operating leverage, such as sales productivity and capacity, functionality and value in our subscription service offerings;
-
growing our sales to businesses, service providers and government organizations, our ability to execute these sales and the complexity of selling to all segments (including the increased competition and unpredictability of timing associated with sales to larger enterprises), the impact of sales to these organizations on our long-term growth, expansion and operating results, and the effectiveness of our sales organization;
-
our ability to hire properly qualified and effective sales, support and engineering employees;
*•*risks and expectations related to acquisitions and equity interests in private and public companies, including integration issues related to product plans and the acquired technology, and risks of negative impact by such acquisitions and equity investments on our financial results;
-
trends in revenue, cost of revenue and gross margin;
-
trends in our operating expenses, including sales and marketing expense, research and development expense, general and administrative expense, and expectations regarding these expenses;
*•*expectations that our operating expense will increase in absolute dollars during 2022;
*•*expectations that proceeds from the exercise of stock options in future years will be adversely impacted by the increased mix of restricted stock units versus stock options granted;
- expectations regarding uncertain tax benefits and our effective domestic and global tax rates, and the impact of the Tax Cuts and Jobs Act and the Coronavirus Aid, Relief, and Economic Security Act (the “CARES Act”);
*•*expectations regarding spending related to real estate acquisitions and development, data center investments, as well as other capital expenditures and to the impact on free cash flow;
- estimates of a range of 2022 spending on capital expenditures;
*•*competition in our markets;
-
statements regarding expected outcomes and liabilities in litigation;
-
our intentions regarding share repurchases and the sufficiency of our existing cash, cash equivalents and investments to meet our cash needs, including our debt servicing requirements, for at least the next 12 months;
*•*other statements regarding our future operations, financial condition and prospects and business strategies; and
*•*adoption and impact of new accounting standards.
These forward-looking statements are subject to certain risks and uncertainties that could cause our actual results to differ materially from those reflected in the forward-looking statements. Factors that could cause or contribute to such differences include, but are not limited to, those discussed in this Annual Report on Form 10-K and, in particular, the risks discussed under the heading “Risk Factors” in Part I, Item 1A of this Annual Report on Form 10-K and those discussed in other documents we file with the SEC. We undertake no obligation, and specifically disclaim any obligation, to revise or publicly release the results of any revision to these and any other forward-looking statements. Given these risks and uncertainties, readers are cautioned not to place undue reliance on such forward-looking statements.
Business Overview
Fortinet is a global leader in cybersecurity solutions provided to a wide variety of organizations, including enterprises, communication service providers and security service providers, government organizations and small businesses. Our cybersecurity solutions are designed to provide broad visibility and segmentation of the digital attack surface through our integrated Fortinet Security Fabric cybersecurity mesh platform, which features automated protection, detection and response along with consolidated visibility across both Fortinet developed solutions and a broad ecosystem of third-party solutions and technologies. The Fortinet Security Fabric cybersecurity mesh platform leverages a common operating system or integration to this operating system across our product offerings and helps organizations better secure their environments and reduce their security and network complexities. The Fortinet Security Fabric has an open architecture designed to connect Fortinet solutions and third-party solutions in a single ecosystem, enabling holistic detection and coordinated response across the attack cycle and surface through integration and automation.
Our product offerings consist of our FortiGate network security physical and virtual products and our non-FortiGate physical and virtual, software, and cloud-hosted products. In addition to high performing security and networking features, we offer a rich set of cloud-delivered security services that can be added to different products across the Fortinet Security Fabric and customized to the organization’s use cases.
Our cloud- and hosted- products and services include sandboxing, endpoint detection and response (“EDR”), email security, web application and API security and cloud networking security as well as Fortinet Security Fabric management and analytics.
Our FortiGuard security services are enabled by FortiGuard Labs, which provides threat research and artificial intelligence capabilities from a cloud network to deliver coordinated protection for the ever-expanding attack surface through FortiGate appliance and virtual machine as well as all Fortinet Security Fabric products that are registered by the end-customer.
Our proprietary Security Processing Units (“SPUs”) are Application-Specific Integrated Circuits that are implemented in our physical FortiGate appliances and are designed to enhance the security processing capabilities implemented in software by accelerating computationally intensive tasks such as firewall policy enforcement, software-defined wide-area network (“SD-WAN”), network address translation, Intrusion Prevention Systems (“IPS”), threat detection and encryption. We also provide virtualized Security Processing Units (“vSPUs”) across our FortiGate virtual appliances to deliver similar accelerated capabilities when run in virtualized environments.
Our FortiOS operating system provides the foundation for the operation of all FortiGate network security appliances, whether physical, virtual, private- or public-cloud based. FortiOS directs the operations of processors and SPUs and provides system management functions. We make regular updates to FortiOS available through our FortiCare support services.
FortiOS, its associated security and networking functions and products that
Showing the first 8K of 88K characters. Open the full section
Item 7A. Quantitative and Qualitative Disclosures about Market Risk
Investment and Interest Rate Fluctuation Risk
We are exposed to interest rate risks related to our investment portfolio and outstanding debt.
The primary objectives of our investment activities are to preserve principal, provide liquidity and maximize income without significantly increasing risk. Some of the securities we invest in are subject to market risk. This means that a change in prevailing interest rates may cause the principal amount of the investment to fluctuate. To minimize this risk, we maintain our portfolio of cash, cash equivalents, investments and marketable equity securities in a variety of securities, including commercial paper, corporate debt securities, U.S. government and agency securities, certificates of deposit and term deposits, money
market funds, municipal bonds and marketable equity securities. The risk associated with fluctuating interest rates is limited to our investment portfolio. A 10% decrease in interest rates in 2021, 2020 and 2019 would have resulted in an insignificant decrease in our interest income in each of these periods.
On March 5, 2021, we issued $1.0 billion aggregate principal amount of senior notes, consisting of $500.0 million aggregate principal amount of 1.0% notes due March 15, 2026 and $500.0 million aggregate principal amount of 2.2% notes due March 15, 2031. We carry the senior notes at face value less unamortized discount on our consolidated balance sheets. As the senior notes bear interest at a fixed rate, we have no financial statement risk associated with changes in interest rates. Refer to Note 11. Debt in Part II, Item 8 of this Annual Report on Form 10-K.
Foreign Currency Exchange Risk
Our sales contracts are primarily denominated in U.S. dollars and therefore substantially all of our revenue is not subject to foreign currency translation risk. However, a substantial portion of our operating expenses incurred outside the United States are denominated in foreign currencies and are subject to fluctuations due to changes in foreign currency exchange rates, particularly changes in the Canadian dollar (“CAD”), the Euro (“EUR”) and the British pound (“GBP”). To help protect against significant fluctuations in value and the volatility of future cash flows caused by changes in currency exchange rates, we engage in foreign currency risk management activities to minimize the impact of balance sheet items denominated in CAD. We do not use these contracts for speculative or trading purposes. All of the derivative instruments are with high quality financial institutions and we monitor the credit worthiness of these parties. These contracts typically have a maturity of one month and settle on the last day of each month. We record changes in the fair value of forward exchange contracts related to balance sheet accounts in other expense—net in the consolidated statements of income. We recognized an expense of $8.2 million in 2021 due to foreign currency transaction losses.
Our use of forward exchange contracts is intended to reduce, but not eliminate, the impact of currency exchange rate movements. Our forward exchange contracts are relatively short-term in nature and are focused on the CAD. Long-term material changes in the value of the U.S. dollar against other foreign currencies, such as the EUR and GBP, could adversely impact our operating expenses in the future. We assessed the risk of loss in fair values from the impact of hypothetical changes in foreign currency exchange rates. For foreign currency exchange rate risk, a 10% increase or decrease of foreign currency exchange rates against the U.S. dollar with all other variables held constant would have resulted in a $8.3 million change in the value of our foreign currency cash balances as of December 31, 2021.
Inflation Risk
Our monetary assets, consisting primarily of cash, cash equivalents and short-term investments, are not affected significantly by inflation because they are predominantly short-term. We believe the impact of inflation on replacement costs of equipment, furniture and leasehold improvements will not materially affect our operations. The rate of inflation, however, affects our cost of revenue and expenses, such as those for employee compensation, which may not be readily recoverable in the price of products and services offered by us.
Item 8. Financial Statements and Supplementary Data
INDEX TO CONSOLIDATED FINANCIAL STATEMENTS
REPORT OF INDEPENDENT REGISTERED PUBLIC ACCOUNTING FIRM
To the stockholders and the Board of Directors of Fortinet, Inc.
Opinion on the Financial Statements
We have audited the accompanying consolidated balance sheets of Fortinet, Inc. and subsidiaries (the “Company”) as of December 31, 2021 and 2020, the related consolidated statements of income, comprehensive income, equity, and cash flows, for each of the three years in the period ended December 31, 2021, and the related notes (collectively referred to as the “financial statements”). In our opinion, the financial statements present fairly, in all material respects, the financial position of the Company as of December 31, 2021 and 2020, and the results of its operations and its cash flows for each of the three years in the period ended December 31, 2021, in conformity with accounting principles generally accepted in the United States of America.
We have also audited, in accordance with the standards of the Public Company Accounting Oversight Board (United States) (PCAOB), the Company’s internal control over financial reporting as of December 31, 2021, based on criteria established in Internal Control – Integrated Framework (2013) issued by the Committee of Sponsoring Organizations of the Treadway Commission and our report dated February 25, 2022, expressed an unqualified opinion on the Company’s internal control over financial reporting.
Basis for Opinion
These financial statements are the responsibility of the Company’s management. Our responsibility is to express an opinion on the Company’s financial statements based on our audits. We are a public accounting firm registered with the PCAOB and are required to be independent with respect to the Company in accordance with the U.S. federal securities laws and the applicable rules and regulations of the Securities and Exchange Commission and the PCAOB.
We conducted our audits in accordance with the standards of the PCAOB. Those standards require that we plan and perform the audit to obtain reasonable assurance about whether the financial statements are free of material misstatement, whether due to error or fraud. Our audits included performing procedures to assess the risks of material misstatement of the financial statements, whether due to error or fraud, and performing procedures that respond to those risks. Such procedures included examining, on a test basis, evidence regarding the amounts and disclosures in the financial statements. Our audits also included evaluating the accounting principles used and significant estimates made by management, as well as evaluating the overall presentation of the financial statements. We believe that our audits provide a reasonable basis for our opinion.
Critical Audit Matters
The critical audit matters communicated below are matters arising from the current-period audit of the financial statements that were communicated or required to be communicated to the audit committee and that (1) relate to accounts or disclosures that are material to the financial statements and (2) involved our especially challenging, subjective, or complex judgments. The communication of critical audit matters does not alter in any way our opinion on the financial statements, taken as a whole, and we are not, by communicating the critical audit matters below, providing separate opinions on the critical audit matters or on the accounts or disclosures to which they relate.
Litigation – Refer to Note 13 to the financial statements
Critical Audit Matter Description
The Company is involved in disputes, litigation and other legal actions in the normal course of business. Claims from third parties may result in a requirement to pay substantial damages and could prevent the Company from selling certain of their products. The Company accrues for a loss contingency if a loss is probable and the amount of the loss can be reasonably estimated. These accruals are generally based on a range of possible outcomes that require significant management judgement.
Given the inherent uncertainty of the outcome of identified current matters, auditing the valuation assertion of litigation contingencies required a high degree of auditor judgment and an increased extent of effort when performing audit procedures.
How the Critical Audit Matter Was Addressed in the Audit
Our audit procedures related to the litigation contingencies included the following, among others:
- We tested the effectiveness of controls over management’s litigation contingency accrual analysis and assessment of matters
with potential impact.
-
We obtained and evaluated legal letters from internal and external legal counsel, and we discussed with internal legal counsel the pending litigation matters.
-
We made inquiries with management to obtain an understanding of litigation matters that the Company is currently undergoing.
-
We read available court filings for litigation matters to search for contradictory information.
-
We read Board of Directors meeting minutes to search for contradictory information.
-
We evaluated the assumptions used by the Company to estimate the litigation contingency, including corroborating the assumptions with internal legal counsel.
Investments in Privately Held Companies – Refer to Notes 1 and 6 to the financial statements
Critical Audit Matter Description
In fiscal year 2021, the Company invested $160 million in cash for shares of the Series A Preferred Stock of Linksys Holdings, Inc.
Showing the first 8K of 160K characters. Open the full section
Item 9. Changes in and Disagreements With Accountants on Accounting and Financial Disclosure
None.
Item 9A. Controls and Procedures
Evaluation of Disclosure Controls and Procedures
Our management, with the participation of our Chief Executive Officer and Chief Financial Officer, evaluated the effectiveness of our disclosure controls and procedures (as defined in Rule 13a-15(e) or 15d-15(e) under the Securities Exchange Act of 1934 (the “Exchange Act”)) as of the end of the period covered by this Annual Report on Form 10-K. In designing and evaluating the disclosure controls and procedures, management recognized that any controls and procedures, no matter how well designed and operated, can provide only reasonable assurance of achieving the desired control objectives. In addition, the design of disclosure controls and procedures must reflect the fact that there are resource constraints and that management is required to apply its judgment in evaluating the benefits of possible controls and procedures relative to their costs.
Based on that evaluation, our Chief Executive Officer and Chief Financial Officer concluded that our disclosure controls and procedures were effective as of December 31, 2021 to provide reasonable assurance that information we are required to disclose in reports that we file or submit under the Exchange Act is recorded, processed, summarized and reported within the time periods specified in SEC rules and forms, and that such information is accumulated and communicated to our management, including our Chief Executive Officer and Chief Financial Officer, as appropriate, to allow timely decisions regarding required disclosure.
Management’s Report on Internal Control over Financial Reporting
Our management is responsible for establishing and maintaining adequate internal control over financial reporting, as defined in Rule 13a-15(f) and 15d-15(f) under the Exchange Act. Management conducted an evaluation of the effectiveness of our internal control over financial reporting based on the framework in Internal Control—Integrated Framework (2013) set forth by the Committee of Sponsoring Organizations of the Treadway Commission.
In accordance with the Internal Controls Guidance, management has excluded Alaxala Networks Corporation (“Alaxala”), a privately-held network hardware equipment company in Japan, from its assessment of internal control over financial reporting as of December 31, 2021, because it was acquired by the Company in a business combination during the fiscal year ended December 31, 2021. Alaxala assets represented approximately 1.5% of the Company’s consolidated total assets, excluding the effects of purchase accounting, as of December 31, 2021 and its revenues represented approximately 1.3% of the Company's consolidated total revenues for the year ended December 31, 2021.
Based on this evaluation, management concluded that our internal control over financial reporting was effective as of December 31, 2021. Management reviewed the results of its assessment with our Audit Committee. The effectiveness of our internal control over financial reporting as of December 31, 2021 has been audited by Deloitte & Touche LLP, an independent registered public accounting firm, as stated in its report, which appears in this Item under the heading “Report of Independent Registered Public Accounting Firm.”
Changes in Internal Control over Financial Reporting
There were no other changes in our internal control over financial reporting (as defined in Rules 13a-15(f) or 15d-15(f) under the Exchange Act) during 2021 that have materially affected, or are reasonably likely to materially affect, our internal control over financial reporting.
REPORT OF INDEPENDENT REGISTERED PUBLIC ACCOUNTING FIRM
To the stockholders and the Board of Directors of Fortinet, Inc.
Opinion on Internal Control over Financial Reporting
We have audited the internal control over financial reporting of Fortinet, Inc. and subsidiaries (the “Company”) as of December 31, 2021, based on criteria established in Internal Control – Integrated Framework (2013) issued by the Committee of Sponsoring Organizations of the Treadway Commission (COSO). In our opinion, the Company maintained, in all material respects, effective internal control over financial reporting as of December 31, 2021, based on criteria established in Internal Control – Integrated Framework (2013) issued by COSO.
We have also audited, in accordance with the standards of the Public Company Accounting Oversight Board (United States) (PCAOB), the consolidated financial statements as of and for the year ended December 31, 2021, of the Company and our report dated February 25, 2022, expressed an unqualified opinion on those financial statements.
As described in “Management’s Report on Internal Control over Financial Reporting”, management excluded from its assessment the internal control over financial reporting at Alaxala Networks Corporation (“Alaxala”), which was acquired on August 31, 2021, and whose financial statements constitute approximately 1.5% of the Company’s consolidated total assets, excluding the effects of purchase accounting, as of December 31, 2021 and approximately 1.3% of the Company’s consolidated total revenues for the year ended December 31, 2021. Accordingly, our audit did not include the assessment of the internal controls over financial reporting for Alaxala.
Basis for Opinion
The Company’s management is responsible for maintaining effective internal control over financial reporting and for its assessment of the effectiveness of internal control over financial reporting, included in the accompanying Management’s Report on Internal Control over Financial Reporting. Our responsibility is to express an opinion on the Company’s internal control over financial reporting based on our audit. We are a public accounting firm registered with the PCAOB and are required to be independent with respect to the Company in accordance with the U.S. federal securities laws and the applicable rules and regulations of the Securities and Exchange Commission and the PCAOB.
We conducted our audit in accordance with the standards of the PCAOB. Those standards require that we plan and perform the audit to obtain reasonable assurance about whether effective internal control over financial reporting was maintained in all material respects. Our audit included obtaining an understanding of internal control over financial reporting, assessing the risk that a material weakness exists, testing and evaluating the design and operating effectiveness of internal control based on the assessed risk, and performing such other procedures as we considered necessary in the circumstances. We believe that our audit provides a reasonable basis for our opinion.
Definition and Limitations of Internal Control over Financial Reporting
A company’s internal control over financial reporting is a process designed to provide reasonable assurance regarding the reliability of financial reporting and the preparation of financial statements for external purposes in accordance with generally accepted accounting principles. A company’s internal control over financial reporting includes those policies and procedures that (1) pertain to the maintenance of records that, in reasonable detail, accurately and fairly reflect the transactions and dispositions of the assets of the company; (2) provide reasonable assurance that transactions are recorded as necessary to permit preparation of financial statements in accordance with generally accepted accounting principles, and that receipts and expenditures of the company are being made only in accordance with authorizations of management and directors of the company; and (3) provide reasonable assurance regarding prevention or timely detection of unauthorized acquisition, use, or disposition of the company’s assets that could have a material effect on the financial statements.
Because of its inherent limitations, internal control over financial reporting may not prevent or detect misstatements. Also, projections of any evaluation of effectiveness to future periods are subject to the risk that controls may become inadequate because of changes in conditions, or that the degree of compliance with the policies or procedures may deteriorate.
/s/ DELOITTE & TOUCHE LLP
San Jose, California
February 25, 2022
Item 9B. Other Information
None.
Item 9C. Disclosure Regarding Foreign Jurisdictions that Prevents Inspections
Not applicable.
Part III
Item 10. Directors, Executive Officers and Corporate Governance
Information responsive to this item is incorporated herein by reference to our definitive proxy statement with respect to our 2022 Annual Meeting of Stockholders to be filed with the SEC within 120 days after the end of the fiscal year covered by this Annual Report on Form 10-K.
As part of our system of corporate governance, our board of directors has adopted a code of business conduct and ethics. The code applies to all of our employees, officers (including our principal executive officer, principal financial officer, principal accounting officer or controller, or persons performing similar functions), agents and representatives, including our independent directors and consultants, who are not our employees, with regard to their Fortinet-related activities. Our code of business conduct and ethics is available on our website at www.fortinet.com under “Corporate—Investor Relations—Corporate Governance.” We will post on this section of our website any amendment to our code of business conduct and ethics, as well as any waivers of our code of business conduct and ethics, that are required to be disclosed by the rules of the SEC or the Nasdaq Stock Market.
Item 11. Executive Compensation
Information responsive to this item is incorporated herein by reference to our definitive proxy statement with respect to our 2022 Annual Meeting of Stockholders to be filed with the SEC within 120 days after the end of the fiscal year covered by this Annual Report on Form 10-K.
Item 12. Security Ownership of Certain Beneficial Owners and Management and Related Stockholder Matters
Information responsive to this item is incorporated herein by reference to our definitive proxy statement with respect to our 2022 Annual Meeting of Stockholders to be filed with the SEC within 120 days after the end of the fiscal year covered by this Annual Report on Form 10-K.
Item 13. Certain Relationships and Related Transactions, and Director Independence
Information responsive to this item is incorporated herein by reference to our definitive proxy statement with respect to our 2022 Annual Meeting of Stockholders to be filed with the SEC within 120 days after the end of the fiscal year covered by this Annual Report on Form 10-K.
Item 14. Principal Accounting Fees and Services
Information responsive to this item is incorporated herein by reference to our definitive proxy statement with respect to our 2022 Annual Meeting of Stockholders to be filed with the SEC within 120 days after the end of the fiscal year covered by this Annual Report on Form 10-K.
Part IV
Item 15. Exhibits and Financial Statement Schedules
(a) The following documents are filed as part of this Annual Report on Form 10-K:
1.Financial Statements: The information concerning Fortinet’s financial statements and the Report of Independent Registered Public Accounting Firm required by this Item 15(a)(1) is incorporated by reference herein to the section of this Annual Report on Form 10-K in Part II, Item 8, titled “Financial Statements and Supplementary Data.”
2. Financial Statement Schedule: Financial statement schedules have been omitted because they are not applicable or are not required or the information required to be set forth therein is included in the consolidated financial statements or notes thereto.
- Exhibits: See Item 15(b) below. We have filed, or incorporated into this Annual Report on Form 10-K by reference, the exhibits listed on the accompanying Exhibit Index immediately preceding the signature page of this Annual Report on Form 10-K.
(b) Exhibits:
The exhibits listed on the Exhibit Index immediately preceding the signature page of this Annual Report on Form 10-K is incorporated herein by reference as the list of exhibits required by this Item 15(b).
(c) Financial Statement Schedules: See Item 15(a) above.
EXHIBIT INDEX
| Exhibit Number | Description | Form Incorporated by reference herein | Date Filed | Exhibit Number | ||||||||||||||||||||||
| 3.1 | Amended and Restated Certificate of Incorporation | Current Report on Form 8-K (File No. 001-34511) | June 28, 2018 | 3.1 | ||||||||||||||||||||||
| 3.2 | Amended and Restated Bylaws | Current Report on Form 8-K (File No. 001-34511) | April 28, 2021 | 3.1 | ||||||||||||||||||||||
| 4.1 | Specimen common stock certificate of the Company | Registration Statement on Form S-l, as amended (File No. 333-161190) | November 2, 2009 | 4.1 | ||||||||||||||||||||||
| 4.2* | Description of Securities Registered Pursuant to Section 12 of the Exchange Act | |||||||||||||||||||||||||
| 10.1† | Forms of Indemnification Agreement between the Company and its directors and officers | Registration Statement on Form S-l (File No. 333-161190) | August 10, 2009 | 10.1 | ||||||||||||||||||||||
| 10.2† | Amended and Restated 2009 Equity Incentive Plan | Quarterly Report on Form 10-Q (File No. 001-34511) | August 1, 2019 | 10.1 | ||||||||||||||||||||||
| 10.3† | Forms of stock option agreement under Amended and Restated 2009 Equity Incentive Plan | Annual Report on Form 10-K (File No. 001-34511) | February 28, 2012 | 10.5 | ||||||||||||||||||||||
| 10.4† | Form of performance stock unit award agreement under Amended and Restated 2009 Equity Incentive Plan | Quarterly Report on Form 10-Q (File No. 001-34511) | August 6, 2013 | 99.1 | ||||||||||||||||||||||
| 10.5† | Forms of restricted stock unit award and performance stock unit award agreement under Amended and Restated 2009 Equity Incentive Plan (Additional Forms) | Annual Report on Form 10-K (File No. 001-34511) | March 2, 2015 | 10.7 | ||||||||||||||||||||||
| 10.6† | Form of restricted stock unit award agreement under Amended and Restated 2009 Equity Incentive Plan (Additional Form) | Annual Report on Form 10-K (File No. 001-34511) | February 26, 2020 | 10.6 | ||||||||||||||||||||||
| 10.7† | Form of stock option award agreement under Amended and Restated 2009 Equity Incentive Plan (Additional Form) | Annual Report on Form 10-K (File No. 001-34511) | February 26, 2020 | 10.7 | ||||||||||||||||||||||
| 10.8† | Fortinet, Inc. Amended Bonus Plan | Annual Report on Form 10-K (File No. 001-34511) | February 19, 2021 | 10.8 | ||||||||||||||||||||||
| 10.9† | Fortinet, Inc. Cash and Equity Incentive Plan | Quarterly Report on Form 10-Q (File No. 001-34511) | November 5, 2013 | 10.1 | ||||||||||||||||||||||
| 10.10† | Form of Change of Control Agreement between the Company and its directors | Quarterly Report on Form 10-Q (File No. 001-34511) | August 4, 2015 | 10.1 | ||||||||||||||||||||||
| 10.11† | Amended and Restated Change of Control Severance Agreement, effective as of August 7, 2019, between the Company and Ken Xie | Quarterly Report on Form 10-Q (File No. 001-34511) | August 1, 2019 | 10.2 | ||||||||||||||||||||||
| 10.12† | Amended and Restated Change of Control Severance Agreement, effective as of August 7, 2019, between the Company and Michael Xie | Quarterly Report on Form 10-Q (File No. 001-34511) | August 1, 2019 | 10.3 | ||||||||||||||||||||||
| 10.13† | Amended and Restated Change of Control Severance Agreement, effective as of August 7, 2019, between the Company and John Whittle | Quarterly Report on Form 10-Q (File No. 001-34511) | August 1, 2019 | 10.4 | ||||||||||||||||||||||
| 10.14† | Offer Letter, dated as of October 23, 2006, by and between the Company and John Whittle | Registration Statement on Form S-l, as amended (File No. 333-161190) | August 10, 2009 | 10.10 | ||||||||||||||||||||||
| 10.15† | Offer Letter, dated as of April 3, 2014, by and between the Company and Keith Jensen | Annual Report on Form 10-K (File No. 001-34511) | February 26, 2018 | 10.22 | ||||||||||||||||||||||
| 10.16† | Amended and Restated Change of Control Severance Agreement, effective as of August 7, 2019, between the Company and Keith Jensen | Quarterly Report on Form 10-Q (File No. 001-34511) | August 1, 2019 | 10.5 | ||||||||||||||||||||||
| 21.1* | List of subsidiaries | |||||||||||||||||||||||||
| 23.1* | Consent of Independent Registered Public Accounting Firm | |||||||||||||||||||||||||
| 24.1* | Power of Attorney (incorporated by reference to the signature page of this Annual Report on Form 10-K) |
| 31.1* | Certification of Chief Executive Officer pursuant to Exchange Act Rules 13a-14(a) and 15d-14(a), as adopted pursuant to Section 302 of the Sarbanes-Oxley Act of 2002 | |||||||
| 31.2* | Certification of Chief Financial Officer pursuant to Exchange Act Rules 13a-14(a) and 15d-14(a), as adopted pursuant to Section 302 of the Sarbanes-Oxley Act of 2002 | |||||||
| 32.1** | Certifications of Chief Executive Officer and Chief Financial Officer pursuant to 18 U.S.C. Section 1350, as adopted pursuant to Section 906 of the Sarbanes-Oxley Act of 2002 | |||||||
| 101.INS* | Inline XBRL Instance Document - the instance document does not appear in the interactive data file because its XBRL tags are embedded within the inline XBRL document. | |||||||
| 101.SCH* | Inline XBRL Taxonomy Extension Schema Document | |||||||
| 101.CAL* | Inline XBRL Taxonomy Extension Calculation Linkbase Document | |||||||
| 101.DEF* | Inline XBRL Taxonomy Extension Definition Linkbase Document | |||||||
| 101.LAB* | Inline XBRL Taxonomy Extension Label Linkbase Document | |||||||
| 101.PRE* | Inline XBRL Taxonomy Extension Presentation Linkbase Document | |||||||
| 104* | Cover Page Interactive Data File - the cover page from the Company’s Annual Report on Form 10-K for the year ended December 31, 2021 is formatted in inline XBRL. |
† Indicates management compensatory plan, contract or arrangement.
- Filed herewith.
** Furnished herewith. This certification is deemed not filed for purposes of Section 18 of the Exchange Act, or otherwise subject to the liability of that section, nor shall it be deemed incorporated by reference into any filing under the Securities Act or the Exchange Act.
Item 16. Form 10-K summary
None.
SIGNATURES
Pursuant to the requirements of Section 13 or 15(d) of the Securities Exchange Act of 1934, the registrant has duly caused this report to be signed on its behalf by the undersigned, thereunto duly authorized, on February 25, 2022.
| FORTINET, INC. | ||||||||
| By: | /s/ Ken Xie | |||||||
| Ken Xie, Chief Executive Officer and Chairman | ||||||||
| (Duly Authorized Officer and Principal Executive Officer) |
| FORTINET, INC. | ||||||||
| By: | /s/ Keith Jensen | |||||||
| Keith Jensen, Chief Financial Officer | ||||||||
| (Duly Authorized Officer and Principal Financial Officer and Principal Accounting Officer) |
POWER OF ATTORNEY
KNOW ALL PERSONS BY THESE PRESENTS, that each person whose signature appears below constitutes and appoints Ken Xie and Keith Jensen, jointly and severally, his or her attorney-in-fact, with the power of substitution, for him or her in any and all capacities, to sign any amendments to this Annual Report on Form 10-K and to file the same, with exhibits thereto and other documents in connection therewith, with the Securities and Exchange Commission, hereby ratifying and confirming all that each of said attorneys-in-fact, or his substitute or substitutes, may do or cause to be done by virtue hereof.
Pursuant to the requirements of the Securities Exchange Act of 1934, this report has been signed below by the following persons on behalf of the registrant and in the capacities and on the dates indicated.
| Signature | Title | Date | ||||||||||||
| /s/ Ken Xie | Chief Executive Officer and Chairman | February 25, 2022 | ||||||||||||
| Ken Xie | (Principal Executive Officer) | |||||||||||||
| /s/ Keith Jensen | Chief Financial Officer | February 25, 2022 | ||||||||||||
| Keith Jensen | (Principal Financial Officer and Principal Accounting Officer) | |||||||||||||
| /s/ Michael Xie | President, Chief Technology Officer and Director | February 25, 2022 | ||||||||||||
| Michael Xie | ||||||||||||||
| /s/ Kelly Ducourty | Director | February 25, 2022 | ||||||||||||
| Kelly Ducourty | ||||||||||||||
| /s/ Kenneth A. Goldman | Director | February 25, 2022 | ||||||||||||
| Kenneth A. Goldman | ||||||||||||||
| /s/ Ming Hsieh | Director | February 25, 2022 | ||||||||||||
| Ming Hsieh | ||||||||||||||
| /s/ Jean Hu | Director | February 25, 2022 | ||||||||||||
| Jean Hu | ||||||||||||||
| /s/ William H. Neukom | Director | February 25, 2022 | ||||||||||||
| William H. Neukom | ||||||||||||||
| /s/ Judith Sim | Director | February 25, 2022 | ||||||||||||
| Judith Sim | ||||||||||||||
| /s/ Admiral James Stavridis | Director | February 25, 2022 | ||||||||||||
| Admiral James Stavridis |