 filings.tools
Equifax 2018 10-K Annual Report
EFX · CIK 33185 · Form 10-K · Fiscal year ended December 31, 2018 · Filed February 21, 2019
22 sections, 567K characters. Original on sec.gov · Markdown · JSON
Risk FactorsBusinessMD&AFinancial StatementsWhat changed vs 2017
Cover and table of contents
10-K 1 efx10k20181231.htm 10-K
UNITED STATES
SECURITIES AND EXCHANGE COMMISSION
Washington, D.C. 20549
FORM 10-K
| ☒ | ANNUAL REPORT PURSUANT TO SECTION 13 OR 15(d) OF THE SECURITIES EXCHANGE ACT OF 1934 |
For the fiscal year ended December 31, 2018
OR
| ☐ | TRANSITION REPORT PURSUANT TO SECTION 13 OR 15(d) OF THE SECURITIES EXCHANGE ACT OF 1934 |
For the transition period from to
Commission File Number 001-06605
EQUIFAX INC.
(Exact name of registrant as specified in its charter)
| Georgia | 58-0401110 | |
| (State or other jurisdiction of incorporation or organization) | (I.R.S. Employer Identification No.) | |
| 1550 Peachtree Street, N.W. | ||
| Atlanta, Georgia | 30309 | |
| (Address of principal executive offices) | (Zip Code) |
Registrant’s telephone number, including area code: 404-885-8000
Securities registered pursuant to Section 12(b) of the Act:
| Title of each class | Name of each exchange on which registered | |
| Common Stock, $1.25 par value per share | New York Stock Exchange |
Securities registered pursuant to Section 12(g) of the Act: None.
Indicate by check mark if Registrant is a well-known seasoned issuer, as defined in Rule 405 of the Securities Exchange Act (“Act”). ☒ YES ☐ NO
Indicate by check mark if Registrant is not required to file reports pursuant to Section 13 or Section 15(d) of the Act. ☐ YES ☒ NO
Indicate by check mark whether Registrant (1) has filed all reports required to be filed by Section 13 or 15(d) of the Securities Exchange Act of 1934 during the preceding 12 months (or for such shorter period that the Registrant was required to file such reports), and (2) has been subject to such filing requirements for the past 90 days. ☒ YES ☐ NO
Indicate by check mark whether the Registrant has submitted electronically every Interactive Data File required to be submitted pursuant to Rule 405 of Regulation S-T during the preceding 12 months (or for such shorter period that the Registrant was required to submit such files). YES ☒ NO ☐
Indicate by check mark if disclosure of delinquent filers pursuant to Item 405 of Regulation S-K is not contained herein, and will not be contained, to the best of Registrant’s knowledge, in definitive proxy or information statements incorporated by reference in Part III of this Form 10-K or any amendment to this Form 10-K. ☐
Indicate by check mark whether the Registrant is a large accelerated filer, an accelerated filer, a non-accelerated filer, a smaller reporting company, or an emerging growth company. See definitions of “large accelerated filer,” “accelerated filer,” “smaller reporting company” and “emerging growth company” in Rule 12b-2 of the Exchange Act. (Check one):
| ☒ Large accelerated filer | ☐ Accelerated filer | ☐ Non-accelerated filer | ☐ Smaller reporting company | ☐ Emerging growth company |
If an emerging growth company, indicate by check mark if the registrant has elected not to use the extended transition period for complying with any new or revised financial accounting standards provided pursuant to Section 13(a) of the Exchange Act. ☐
Indicate by check mark whether the Registrant is a shell company (as defined in Rule 12b-2 of the Act). ☐ YES ☒ NO
As of June 30, 2018, the aggregate market value of Registrant’s common stock held by non-affiliates of Registrant was approximately $15,064,356,603 based on the closing sale price as reported on the New York Stock Exchange. At January 31, 2019, there were 120,699,888 shares of Registrant’s common stock outstanding.
DOCUMENTS INCORPORATED BY REFERENCE
Portions of Registrant’s definitive proxy statement for its 2019 annual meeting of shareholders are incorporated by reference in Part III of this Form 10-K.
TABLE OF CONTENTS
PART I
Item 1. BUSINESS
Overview
Equifax Inc. is a global data, analytics and technology company. We provide information solutions and human resources business-process outsourcing services for businesses, governments and consumers. We have a large and diversified group of clients, including financial institutions, corporations, governments and individuals. Our services are based on comprehensive databases of consumer and business information derived from numerous sources including credit, financial assets, telecommunications and utility payments, employment, income, demographic and marketing data. We use advanced statistical techniques, machine learning and proprietary software tools to analyze available data to create customized insights, decision-making solutions and processing services for our clients. We also provide information, technology and services to support debt collections and recovery management. Additionally, we are a leading provider of payroll-related and human resource management business process outsourcing services in the United States of America (U.S.). For consumers, we provide products and services to help people understand, manage and protect their personal information and make more informed financial decisions.
We currently operate in four global regions: North America (U.S. and Canada), Asia Pacific (Australia, New Zealand and India), Europe (the United Kingdom (U.K.), Spain and Portugal) and Latin America (Argentina, Chile, Costa Rica, Ecuador, El Salvador, Honduras, Mexico, Paraguay, Peru and Uruguay). We maintain support operations in the Republic of Ireland, Chile, Costa Rica and India. We also offer Equifax-branded credit services in Russia and India through joint ventures, have investments in consumer and/or commercial credit information companies through joint ventures in Cambodia, Malaysia, Singapore and the United Arab Emirates, and have an investment in a consumer and commercial credit information company in Brazil.
Equifax was originally incorporated under the laws of the State of Georgia in 1913, and its predecessor company dates back to 1899. As used herein, the terms Equifax, the Company, we, our and us refer to Equifax Inc., a Georgia corporation, and its consolidated subsidiaries as a combined entity, except where it is clear that the terms mean only Equifax Inc.
We are organized and report our business results in four operating segments, as follows:
| • | U.S. Information Solutions (USIS) — provides consumer and commercial information solutions to businesses in the U.S. including online information, decisioning technology solutions, fraud and identity management services, analytical services, portfolio management services, mortgage reporting and marketing services. |
| • | International — provides products and services similar to those available in the USIS operating segment but with variations by geographic region. We also provide information, technology and services to support debt collections and recovery management. This operating segment is comprised of our Canada, Europe, Latin America and Asia-Pacific business units. |
| • | Workforce Solutions — provides services enabling customers to verify income and employment (Verification Services) of people in the U.S., as well as providing our customers services to outsource and automate the performance of certain payroll-related and human resource management business processes, including unemployment claims management, tax credits and incentives and I-9 and W-2 form management services and services to allow employers to ensure compliance with the Affordable Care Act (Employer Services). Workforce Solutions is in the process of establishing Verifications Services operations in Canada and Australia. |
| • | Global Consumer Solutions — provides products to consumers in the U.S., Canada and the U.K., enabling them to understand and monitor their credit and monitor and help protect their identity. We also sell consumer credit information to resellers who combine our information with other information to provide direct-to-consumer monitoring, reports and scores. |
2017 Cybersecurity Incident
In 2017, we experienced a cybersecurity incident following a criminal attack on our systems that involved the theft of certain personally identifiable information of U.S., Canadian and U.K. consumers. Criminals exploited a software vulnerability in a U.S. website application to gain unauthorized access to our network. In March 2017, the U.S. Department of Homeland Security distributed a notice concerning the software vulnerability. We undertook efforts to identify and remediate vulnerable
systems; however, the vulnerability in the website application that was exploited was not identified by our security processes. We discovered unusual network activity in late-July 2017 and upon discovery promptly investigated the activity. Once the activity was identified as potential unauthorized access, we acted to stop the intrusion and engaged a leading, independent cybersecurity firm to conduct a forensic investigation to determine the scope of the unauthorized access, including the specific information impacted. Based on our forensic investigation, the unauthorized access occurred from mid-May 2017 through July 2017. No evidence was found that the Company’s core consumer, employment and income, or commercial reporting databases were accessed. We continue to cooperate with law enforcement in connection with the criminal investigation into the actors responsible for the 2017 cybersecurity incident.
The Company has taken actions to provide consumers with tools to protect credit data. Immediately following the announcement of the 2017 cybersecurity incident, the Company devoted substantial resources to notify people of the incident and to provide free services to assist people in monitoring their credit and identity information. This included making its TrustedID® Premier service, an identity theft protection and credit file monitoring product, available for free to all U.S. consumers for twelve months for those who signed up by January 31, 2018. In late 2018, the Company extended the free credit file monitoring services for impacted consumers in the U.S. using the free TrustedID Premier® service by providing them the opportunity to enroll in Experian® IDNotify™ at no cost for an additional twelve months. Similarly, for impacted consumers in Canada and the U.K., we provided free credit reports and scores, credit monitoring and identity theft protection for twenty four months. As part of our commitment to providing long-term resources and protections for consumers, in January 2018, the Company introduced Lock & Alert™, a mobile application enabled service that allows U.S. consumers to quickly lock and unlock their Equifax credit report for free, for life.
As a result of the 2017 cybersecurity incident, we are party to numerous lawsuits and governmental investigations. See “Item 1A. Risk Factors” and “Item 3. Legal Proceedings” in this Form 10-K for more information regarding these lawsuits and investigations.
Our Business Strategy
Our vision is to be a trusted global leader in data, advanced analytics and technology that creates innovative solutions and insights for our customers. Our business strategy is driven by the following imperatives:
| • | Lead our industry in data security. Building on the progress we made following the 2017 cybersecurity incident, we are focused on becoming a leader in our industry in the effectiveness of our data and technology security practices. This includes building an Equifax culture that considers data and technology security, and more broadly risk management, as a primary requirement in all decisions. This also includes the extensive use of advanced data and technology security tools, techniques, services and processes in order to enhance our ability to pro |
Showing the first 8K of 65K characters. Open the full section
Item 1A. RISK FACTORS
All of the risks and uncertainties described below and the other information included in this Form 10-K should be considered and read carefully. The risks described below are not the only ones facing us. The occurrence of any of the following risks or additional risks and uncertainties not presently known to us or that we currently believe to be immaterial could materially and adversely affect our business, financial condition or results of operations. This Form 10-K also contains forward-looking statements and estimates that involve risks and uncertainties. Our actual results could differ materially from those anticipated in the forward-looking statements as a result of specific factors, including the risks and uncertainties described below.
Security breaches like the 2017 cybersecurity incident and other disruptions to our information technology infrastructure could compromise Company, consumer and customer information, interfere with our operations, cause us to incur significant costs for remediation and enhancement of our IT systems and expose us to legal liability, all of which could have a substantial negative impact on our business and reputation.
In the ordinary course of business, we collect, process, transmit and store sensitive data, including intellectual property, proprietary business information and personally identifiable information of consumers. The secure operation of our information technology networks and systems, and of the processing and maintenance of this information, is critical to our business operations and strategy. Despite our substantial investment in physical and technological security measures, employee training and contractual precautions, our information technology networks and infrastructure (or those of our third-party vendors and other service providers) are potentially vulnerable to unauthorized access to data or breaches of confidential information due to criminal conduct, attacks by hackers, employee or insider malfeasance and/or human error.
In 2017, we were the target of a cybersecurity attack that involved the theft of certain personally identifiable information of approximately 145.5 million U.S. consumers, approximately 19,000 Canadian consumers and approximately 860,000 U.K. consumers. In addition, we identified approximately 2.4 million U.S. consumers whose name and partial driver’s license information were stolen in the attack. While the forensic analysis of the 2017 cybersecurity incident is complete, it is possible that further analysis will identify additional consumers affected or additional types of data accessed, which could result in additional notifications and negative publicity.
Following the 2017 cybersecurity incident, we began undertaking significant remediation efforts and other steps to enhance our data security infrastructure which are ongoing. In connection with these efforts, we have incurred significant costs and expect to incur additional significant costs as we continue to enhance our data security infrastructure and take further steps to prevent unauthorized access to our systems and the data we maintain. Despite these efforts, we cannot assure you that all potential causes of this incident have been identified and remediated and that similar cyber incidents will not occur in the future.
Because our products and services involve the storage and transmission of personal information of consumers, we will continue to routinely be the target of attempted cyber and other security threats by outside third parties, including technically sophisticated and well-resourced bad actors attempting to access or steal the data we store. As we transition to cloud-based technologies, we may be exposed to additional cyber threats as we migrate our data from our legacy systems to cloud-based solutions. Our increased dependence on third parties to store our cloud-based data systems may also subject us to further cyber threats. Insider or employee cyber and security threats are also a significant concern for all companies, including ours. In addition, the 2017 cybersecurity incident may embolden individuals or groups to target our systems.
We must continuously plan, develop and monitor our information technology networks and infrastructure to identify, protect, detect, respond to and recover from the risk of unauthorized access, misuse, malware, phishing and other events that could have a security impact. If we experience additional breaches of our security measures, including from incidents that we fail to detect for a period of time, sensitive data may be accessed, stolen, disclosed or lost. Any such access, disclosure or other loss of information could subject us to significant additional litigation, regulatory fines, penalties, losses of customers or reputational damage, any of which could have a significant negative impact on our cash flows, competitive position, financial condition or results of operations.
We cannot ensure that our insurance policies in the future will be adequate to cover losses from any future failures. Our $125.0 million cybersecurity insurance policy was not adequate to cover the losses we have incurred to date from the 2017 cybersecurity incident, and all future losses we incur as a result of the incident will not be covered by insurance. In addition, our insurance coverage will vary from time to time in both type and amount depending on availability, cost and our decisions with respect to risk retention.
The government investigations and litigation resulting from the 2017 cybersecurity incident will continue to adversely impact our business and results of operations.
As a result of the 2017 cybersecurity incident, we are currently a party to a consolidated multi-district consumer class action lawsuit and a consolidated multi-district financial institution class action lawsuit, as well as a consolidated securities class action lawsuit, shareholder derivative litigation and other lawsuits and claims arising out of the 2017 cybersecurity incident seeking monetary damages or other relief. A number of U.S. federal, state, local and foreign governmental officials and agencies, including Congressional committees, the FTC, the CFPB, the SEC, the U.S. Department of Justice and state attorneys general offices in the U.S., the FCA in the U.K. and the Office of the Privacy Commissioner in Canada, continue to investigate events related to the 2017 cybersecurity incident, including how it occurred, the consequences thereof and our response thereto. While we believe it is beneficial to resolve the consolidated multi-district consumer class action and one or more of the government investigations in the U.S. through a global resolution, the complexity of achieving a multi-party resolution, especially involving multiple government agencies, makes this a difficult objective to achieve. We may not have success in achieving a global resolution or even a resolution of any of these matters individually. In addition, other lawsuits, investigations and reports related to the 2017 cybersecurity incident may be filed, commenced or issued. The claims and investigations have resulted in the incurrence of significant external and internal legal costs and expenses and reputational damage to our business and are expected to continue throughout 2019 and beyond. The resolution of these matters may result in damages, costs, fines or penalties substantially in excess of our insurance coverage, which, depending on the amount, could have a material adverse effect on our liquidity or compliance with our credit agreements. If such damages, costs, fines or penalties were great enough that we could not pay them through funds generated from operating activities and/or cause a default under our revolving credit facility, we may be forced to renegotiate or obtain a waiver under our revolving credit facility and/or seek additional debt or equity financing. Such renegotiation or financing may not be available
Showing the first 8K of 64K characters. Open the full section
Item 1B. UNRESOLVED STAFF COMMENTS
None.
Item 2. PROPERTIES
Our executive offices are located at 1550 Peachtree Street, N.W., Atlanta, Georgia. Our other properties are geographically distributed to meet sales and operating requirements worldwide. We consider these properties to be both suitable and adequate to meet our current operating requirements. We ordinarily lease office space for conducting our business and are obligated under approximately 100 leases and other rental arrangements for our field locations. We owned 8 office buildings at December 31, 2018, including our executive offices, one campus which houses our Alpharetta, Georgia data center, a building utilized by our Workforce Solutions operations located in St. Louis, Missouri, as well as three buildings utilized by our Latin America operations located in Mexico City, Mexico and Asuncion, Paraguay.
For additional information regarding our obligations under leases, see Note 6 of the Notes to Consolidated Financial Statements in this Form 10-K. We believe that suitable additional space will be available to accommodate our future needs.
Item 3. LEGAL PROCEEDINGS
Litigation and Investigations related to the 2017 Cybersecurity Incident
Since the 2017 cybersecurity incident, hundreds of class actions and other lawsuits have been filed against us typically alleging harm from the 2017 cybersecurity incident and seeking various remedies, including monetary and injunctive relief. We dispute the allegations in the complaints described below and intend to defend against such claims. In addition, numerous governmental agencies are investigating us in connection with the 2017 cybersecurity incident, which may result in fines, settlements or other relief. Set forth below are descriptions of the main categories of these lawsuits and investigations.
Multidistrict Litigation. Hundreds of class actions were filed against us in federal and state courts relating to the 2017 cybersecurity incident. The plaintiffs in these cases, who purport to represent various classes of U.S. consumers and small businesses, generally claim to have been harmed by alleged actions and/or omissions by Equifax in connection with the 2017 cybersecurity incident and assert a variety of common law and statutory claims seeking monetary damages, injunctive relief and other related relief.
In addition, certain class actions have been filed by financial institutions that allege their businesses have been placed at risk due to the 2017 cybersecurity incident and generally assert various common law claims such as claims for negligence and breach of contract, as well as, in some cases, statutory claims. The financial institution class actions seek compensatory damages, injunctive relief and other related relief.
Furthermore, a lawsuit has been filed against us by the City of Chicago with respect to the 2017 cybersecurity incident alleging violations of state laws and local ordinances governing protection of personal data, consumer fraud, breach notice requirements and business practices and seeking declaratory and injunctive relief and the imposition of fines the aggregate amount of which the complaint does not specifically quantify. Three Indian Tribes filed suits in federal court asserting putative class actions relating to the 2017 cybersecurity incident brought on behalf of themselves and other similarly situated federally recognized Indian Tribes and Nations. Additionally, the Commonwealth of Puerto Rico filed an action on its own behalf and on behalf of the people of Puerto Rico arising out of the 2017 cybersecurity incident.
Beginning on December 6, 2017 and pursuant to multiple subsequent orders, the U.S. Judicial Panel on Multidistrict Litigation ordered the consolidation and transfer for pre-trial proceedings with respect to the U.S. cases pending in federal court discussed above, including the City of Chicago action, the Indian Tribal suits, and the Puerto Rico action, to the Northern District of Georgia as the single U.S. District Court for centralized pre-trial proceedings (the “MDL Court”). Based on these orders, consolidated proceedings with respect to U.S. consumer and financial institution federal class actions and other lawsuits related to the 2017 cybersecurity incident have been conducted in the MDL Court. The MDL Court has established separate tracks for the consumer and financial institution class action cases and appointed lead counsel on behalf of plaintiffs in both tracks. Certain individual plaintiffs with cases pending in the MDL consolidated proceedings, including Puerto Rico and the City of Chicago, have sought the establishment of additional tracks and other related relief. The MDL Court has not yet ruled on those requests.
The Company moved to dismiss the consolidated class action complaints filed by the U.S. consumer, small business and financial institution plaintiffs in their entirety. On January 28, 2019, the MDL Court dismissed the small businesses’ consolidated class action complaint in its entirety. The MDL Court dismissed certain claims brought by the consumer and financial institution plaintiffs, while allowing other claims by those plaintiffs to proceed. Pursuant to case management orders issued by the MDL Court, consolidated pre-trial proceedings, including discovery between the parties, will proceed on the remaining claims of the U.S. consumer and financial institution plaintiffs.
Georgia State Court Consumer Class Actions. Four putative class actions arising from the 2017 cybersecurity incident were filed against us in Fulton County Superior Court and Fulton County State Court in Georgia based on similar allegations and theories as alleged in the U.S. consumer class actions pending in the MDL Court and seek monetary damages, injunctive relief and other related relief on behalf of Georgia citizens. These cases have been transferred to a single judge in the Fulton County Business Court and three of the cases were consolidated into a single action. On July 27, 2018, the Fulton County Business Court granted the Company’s motion to stay the remaining single case, and on August 17, 2018, the Fulton County Business Court granted the Company’s motion to stay the consolidated case.
Canadian Class Actions. Seven Canadian class actions, five of which are on behalf of a national class of approximately 19,000 Canadian consumers, have been filed against us in Ontario, Saskatchewan, Quebec and British Columbia. Each of the proposed Canadian class actions asserts a number of common law and statutory claims seeking monetary damages and other related relief in connection with the 2017 cybersecurity incident. The plaintiffs in each case seek
class certification/authorization on behalf of Canadian consumers whose personal information was allegedly impacted by the 2017 cybersecurity incident. In some cases, plaintiffs also seek class certification on behalf of Canadian consumers who had contracts for subscription products with Equifax around the time of the incident. All purported class actions are at preliminary stages, and we are opposing class certification or authorization in cases where such motions are pending. In addition, one of the cases in Ontario as well as the Saskatchewan case have been stayed. The Court’s order staying the Saskatchewan case is on appeal.
TransUnion Litigation. On November 27, 2017, Trans Union LLC and TransUnion Interactive, Inc. (collectively, “TransUnion”) filed a lawsuit in the U.S. District Court for the Northern District of Illinois against Equifax Information Services LLC, Equifax Inc., and Equifax Consumer Services LLC f/k/a Equifax Consumer Services, Inc. In its lawsuit, TransUnion asserts claims for declaratory relief, breach of contract, and anticipatory repudiation of contract based on our Reciprocal Data Supply Agreement (the “Agreement”), which sets forth the pricing terms for credit monitoring supplied by the parties to each other. TransUnion seeks a declaration regarding its contractual rights under the Agreement and monetary damages. On January 26, 2018, we moved to dismiss TransUnion’s claims. On June 19, 2018, the court granted in part and denied in part our motion to dismiss, dismissing Equifax Inc. from the case. Discovery has now commenced and is scheduled to end in March 2019. We dispute the allegations by TransUnion and intend to defend against its claims.
Securities Class Action Litigation. A consolidated putative class action lawsuit alleging violations of various federal securities laws in connection with statements and alleged omissions regarding our cybersecurity systems and controls is pending against us and certain of our current and former executives, officers and directors in the U.S. District Court for the Northern District of Georgia. The consolidated complaint seeks certification of a class of all persons who purchased or otherwise acquired Equifax securities from February 25, 2016 through September 15, 2017 and unspecified monetary damages, costs and attorneys’ fees. The Company moved to dismiss the consolidated class action complaint in its entirety. On January 28, 2019, the court dismissed claims against certain individual defendants and claims challenging certain statements, but allowed other claims against Equifax and our former Chairman and Chief Executive Officer to proceed. Pursuant to scheduling and case management orders issued by the court, pre-trial proceedings, including discovery between the parties, will proceed on the remaining claims.
Shareholder Derivative Litigation. A consolidated putative shareholder derivative action naming certain of our current and former executives, officers and directors as defendants and naming us as a nominal defendant is pending in the U.S. District Court for the Northern District of Georgia. Among other things, the consolidated complaint alleges claims for breaches of fiduciary duties, unjust enrichment, corporate waste and insider selling by certain defendants, as well as certain claims under the federal securities laws. The complaint seeks unspecified damages on behalf of the Company, plus certain equitable relief. We have appointed a committee of independent directors empowered to evaluate and respond in our best interests to the claims and related litigation demands.
Government Lawsuits. In addition to the City of Chicago’s and Commonwealth of Puerto Rico’s lawsuits in the MDL Court, the City of San Francisco filed a lawsuit against us in Superior Court in the City of San Francisco on behalf of the People of the State of California alleging violations of California’s unfair competition law due to purported violations of statutory protections of personal data and statutory data breach requirements and seeking statutory penalties, injunctive relief, and restitution for California consumers, among other relief. The court has stayed the City of San Francisco action until March 29, 2019.
Civil enforcement actions have been filed against us by the Attorneys General of Massachusetts and West Virginia alleging violations of commonwealth/state consumer protection laws. The Massachusetts action is pending in Suffolk Superior Court and seeks permanent injunctive relief, civil penalties, restitution, disgorgement of profits, costs and attorneys’ fees. The Suffolk Superior Court denied the Company’s motions to stay and dismiss the case, and the case is in discovery. The West Virginia action is pending in the Circuit Court of Boone County and seeks civil penalties and attorneys’ fees. Equifax’s motion to stay proceedings was granted on a temporary basis on December 21, 2018, and then continued on January 24, 2019, with the court scheduling a further hearing for February 28, 2019. The lawsuit filed by the Attorney General of Puerto Rico was transferred to the MDL proceeding, as described above. The Puerto Rico Department of Consumer Affairs has issued Notices of Infraction related to the Company’s alleged failure to give timely notice of the data breach under Puerto Rico law to the Department and Puerto Rico consumers.
Individual Consumer Litigation. Over 1,000 individual consumer actions, including multi-plaintiff actions, have been filed against us in state (general jurisdiction and small claims) and federal courts across the U.S. related to the 2017 cybersecurity incident. These claims include more than 2,500 individual plaintiffs. In addition, there are approximately 50 individual arbitration claims. The plaintiffs/claimants in these cases generally claim to have been harmed by alleged actions and/or omissions by Equifax in connection with the 2017 cybersecurity incident and assert a variety of common law and
statutory claims seeking primarily monetary damages. Where possible, actions filed in federal court or removed to federal court have been noticed for transfer to the MDL Court. Some of these matters have been finally resolved, and others are in various stages.
Government Investigations. We continue to cooperate with federal, state, city and foreign governmental agencies and officials investigating or otherwise seeking information, testimony and/or documents, including through Civil Investigative Demands and subpoenas, regarding the 2017 cybersecurity incident and related matters, including 48 state Attorneys General offices, the District of Columbia, the Federal Trade Commission (“FTC”), the Consumer Financial Protection Bureau (“CFPB”), the U.S. Securities and Exchange Commission (“SEC”), the U.S. Department of Justice, other U.S. state regulators, certain Congressional committees of both the U.S. Senate and House of Representatives, the Office of the Privacy Commissioner of Canada (“OPC”) and the U.K.’s Financial Conduct Authority (“FCA”). The Financial Industry Regulatory Authority, Inc. conducted an investigation that has now been concluded.
With respect to state Attorneys General investigations, the Company is cooperating with a consolidated multi-state investigation involving the Attorneys General of 46 states and the District of Columbia. As noted above, the Attorneys General of Massachusetts, West Virginia and Puerto Rico are not participating in the multi-state process and have filed suit. The Attorneys General of Indiana and Texas are each conducting separate investigations.
The staffs of the CFPB and FTC have informed us that their respective agencies intend to seek injunctive relief damages and, with respect to the CFPB, civil money penalties against us based on allegations related to the 2017 cybersecurity incident. We have submitted written responses to the CFPB and FTC addressing their allegations, and we continue to cooperate with the agencies in their investigations. On October 2, 2018, the Enforcement Staff of the NYDFS provided us with notice that it is considering recommending that the NYDFS take legal action against us, potentially seeking consumer relief and civil money penalties. We continue to cooperate with the NYDFS in its investigation.
The staff of the OPC has informed us that the OPC intends to make certain findings and recommendations in connection with its investigation of the 2017 cybersecurity incident. We have submitted written responses to the OPC and we continue to cooperate in its investigation.
The SEC issued a subpoena on May 14, 2018 regarding disclosure issues relating to the 2017 cybersecurity incident. We continue to cooperate with the SEC in its investigation. In addition, we continue to cooperate with the SEC and the U.S. Attorney’s Office for the Northern District of Georgia regarding investigations into the trading activities by certain of our current and former employees in relation to the 2017 cybersecurity incident.
The New York State Attorney General Investor Protection Bureau (“IPB”) issued a subpoena on September 20, 2017 relating to an investigation of whether there has been a violation of the Martin Act. We continue to cooperate with the IPB in its investigation.
The FCA served an Enforcement Notice and Information Requests. We have provided responses to these requests and continue to cooperate with the FCA.
Although we are actively cooperating with the above investigations and inquiries, an adverse outcome to any such investigations and inquiries could subject us to fines or other obligations, which may have an adverse effect on how we operate our business or our results of operations.
Public Records Litigation
Equifax has been named as a defendant in 19 putative class action lawsuits pending in federal courts across the country relating to its reporting of civil judgments and tax liens on consumers’ credit files. In October 2018, Equifax and the plaintiffs’ attorneys who filed the lawsuits reached an agreement in principle to settle the public records-related claims at issue on behalf of a nationwide class of consumers and we accrued an estimate of our liability for these matters in the third quarter of 2018. The amount accrued represents our best estimate of the liability related to this matter and is not material to the Consolidated Financial Statements. The parties have filed notices of settlement in the pending lawsuits and have begun drafting a settlement agreement and preliminary approval papers to file with the requisite court. If the final terms of a settlement agreement cannot be agreed upon, or if the settlement is not ultimately approved by the court, Equifax believes it has valid defenses to each of these actions and will continue to defend against them.
ACCC Investigation
In March 2017, the Australian Competition and Consumer Commission (the “ACCC”) commenced an investigation to determine whether the Company has been or is engaged in unlawful acts or practices relating to advertising, marketing and sale of consumer reports, credit scores or credit monitoring products in violation of the Australian Consumer Law, which prohibits misleading or deceptive conduct and false representations. The ACCC issued a number of notices to produce documents and information. On March 16, 2018, the ACCC commenced proceedings against the Company. The proceedings were settled on October 2, 2018. The settlement, which is subject to final court review, requires Equifax to, among other things, pay a monetary penalty, provide refunds to certain impacted consumers and refrain from engaging in specified conduct.
California Bankruptcy Litigation
In consolidated actions filed in the U.S. District Court for the Central District of California, captioned Terri N. White, et al. v. Equifax Information Services LLC, Jose Hernandez v. Equifax Information Services LLC, Kathryn L. Pike v. Equifax Information Services LLC, and Jose L. Acosta, Jr., et al. v. Trans Union LLC, et al., plaintiffs asserted that Equifax violated federal and state law (the FCRA, the California Credit Reporting Act and the California Unfair Competition Law) by failing to follow reasonable procedures to determine whether credit accounts are discharged in bankruptcy, including the method for updating the status of an account following a bankruptcy discharge. On August 20, 2008, the District Court approved a Settlement Agreement and Release providing for certain changes in the procedures used by defendants to record discharges in bankruptcy on consumer credit files. That settlement resolved claims for injunctive relief, but not plaintiffs’ claims for damages. On May 7, 2009, the District Court issued an order preliminarily approving an agreement to settle remaining class claims. The District Court subsequently deferred final approval of the settlement and required the settling parties to send a supplemental notice to those class members who filed a claim and objected to the settlement or opted out, with the cost for the re-notice to be deducted from the plaintiffs’ counsel fee award. Mailing of the supplemental notice was completed on February 15, 2011 and the deadline for this group of settling plaintiffs to provide additional documentation to support their damage claims or to opt-out of the settlement was March 31, 2011. On July 15, 2011, the District Court approved the settlement. Several objecting plaintiffs subsequently filed notices of appeal to the U.S. Court of Appeals for the Ninth Circuit, which, on April 22, 2013, issued an order vacating the settlement and remanding the case to the District Court for further proceedings. On January 21, 2014, the District Court denied the objecting plaintiffs’ motion to disqualify counsel for the settling plaintiffs and granted the motion of counsel for the settling plaintiffs to be appointed as interim lead class counsel. On March 28, 2016, the U.S. Court of Appeals for the Ninth Circuit affirmed the District Court’s lead counsel appointment. On January 9, 2017, the United States Supreme Court denied the objectors’ Petition for a Writ of Certiorari. The parties re-engaged in settlement discussions, including participation in mediations in August 2016 and November 2016, and reached an agreement to again settle the monetary claims. Settlement documents were filed with the District Court on April 14, 2017. On June 16, 2017, the Court granted preliminary approval of the proposed settlement, conditionally certified the settlement class, and appointed class counsel and administrator. A Final Fairness Hearing was held on December 11, 2017 and on April 6, 2018, the Court granted final approval. A Notice of Appeal was filed on May 7, 2018. Following the Notice of Appeal, the parties reached a Stipulation Regarding Attorneys’ Fees and Costs with the District Court subject to affirmance of the settlement with the U.S. Court of Appeals for the Ninth Circuit. The Ninth Circuit issued a briefing schedule on July 3, 2018, and on September 17, 2018, the objectors filed their appellate brief. The settling parties filed responsive briefs on January 31, 2019.
Other
Equifax has been named as a defendant in various other legal actions, including administrative claims, regulatory matters, government investigations, class actions and other litigation arising in connection with our business. Some of the legal actions include claims for substantial compensatory or punitive damages or claims for indeterminate amounts of damages. We believe we have defenses to and, where appropriate, will contest, many of these matters. Given the number of these matters, some are likely to result in adverse judgments, penalties, injunctions, fines or other relief. We may explore potential settlements before a case is taken through trial because of the uncertainty and risks inherent in the litigation process.
For information regarding our accounting for legal contingencies, see Note 6 of the Notes to Consolidated Financial Statements in this Form 10-K.
Item 4. MINE SAFETY DISCLOSURES
Not applicable.
PART II
Item 5. MARKET FOR THE REGISTRANT’S COMMON EQUITY, RELATED STOCKHOLDER MATTERS AND ISSUER PURCHASES OF EQUITY SECURITIES
Equifax’s common stock is traded on the New York Stock Exchange under the symbol “EFX.” As of January 31, 2019, Equifax had approximately 3,330 holders of record; however, Equifax believes the number of beneficial owners of common stock exceeds this number.
Shareholder Return Performance Graph
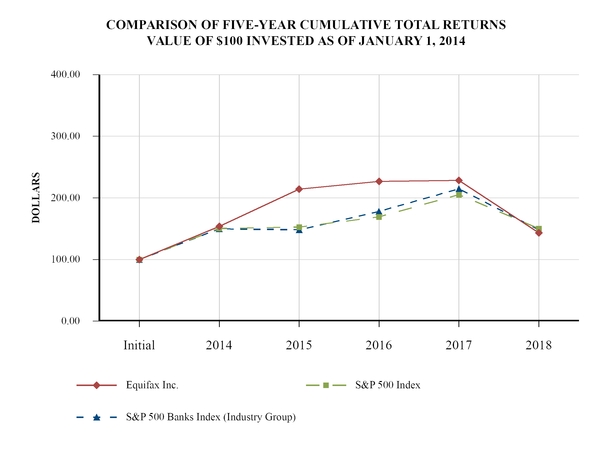
The graph below compares Equifax’s five-year cumulative total shareholder return with that of the Standard & Poor’s Composite Stock Index (S&P 500) and a peer group index, the S&P 500 Banks Index (Industry Group). The graph assumes that the value of the investment in our Common Stock and each index was $100 on the last trading day of 2013 and that all quarterly dividends were reinvested without commissions. Our past performance may not be indicative of future performance.
COMPARATIVE FIVE-YEAR CUMULATIVE TOTAL RETURN AMONG EQUIFAX INC., S&P 500 INDEX, AND S&P 500 BANKS INDEX (INDUSTRY GROUP)
| Fiscal Year Ended December 31, | |||||||||||||||||
| Initial | 2014 | 2015 | 2016 | 2017 | 2018 | ||||||||||||
| Equifax Inc. | 100.00 | 153.68 | 214.06 | 226.90 | 228.22 | 143.32 | |||||||||||
| S&P 500 Index | 100.00 | 150.51 | 152.59 | 169.24 | 205.24 | 150.33 | |||||||||||
| S&P 500 Banks Index (Industry Group) | 100.00 | 149.79 | 148.23 | 178.13 | 214.75 | 148.30 |
The table below contains information with respect to purchases made by or on behalf of Equifax of its common stock during the fourth quarter ended December 31, 2018:
Issuer Purchases of Equity Securities
| Period | Total Number of Shares Purchased (1) | Average Price Paid Per Share (2) | Total Number of Shares Purchased as Part of Publicly-Announced Plans or Programs | Maximum Number (or Approximate Dollar Value) of Shares that May Yet Be Purchased Under the Plans or Programs (3) | ||||||||||
| October 1 - October 31, 2018 | 540 | $ | — | — | $ | 590,092,166 | ||||||||
| November 1 - November 30, 2018 | 295 | $ | — | — | $ | 590,092,166 | ||||||||
| December 1 - December 31, 2018 | 7,044 | $ | — | — | $ | 590,092,166 | ||||||||
| Total | 7,879 | $ | — | — | $ | 590,092,166 |
| (1) | The total number of shares purchased includes, if applicable: (a) shares purchased pursuant to our publicly-announced share repurchase program, or Program; and (b) shares surrendered, or deemed surrendered, in satisfaction of the exercise price and/or to satisfy tax withholding obligations in connection with the exercise of employee stock options and vesting of restricted stock, totaling 540 shares for the month of October 2018, 295 shares for the month of November 2018 and 7,044 shares for the month of December 2018. |
| (2) | Average price paid per share for shares purchased as part of our Program (includes brokerage commissions). |
| (3) | We did not repurchase any common shares during the twelve months ended December 31, 2018. At December 31, 2018, the amount authorized for future share repurchases under the Program was $590.1 million. |
Information relating to compensation plans under which the Company’s equity securities are authorized for issuance is included in the section captioned “Equity Compensation Plan Information” in our 2019 Proxy Statement and is incorporated herein by reference.
Item 6. SELECTED FINANCIAL DATA
The table below summarizes our selected historical financial information for each of the last five years. The summary of operations data for the years ended December 31, 2018, 2017, and 2016, and the balance sheet data as of December 31, 2018 and 2017, have been derived from our audited Consolidated Financial Statements included in this report. The summary of operations data for the years ended December 31, 2015 and 2014, and the balance sheet data as of December 31, 2016, 2015 and 2014, have been derived from our audited Consolidated Financial Statements not included in this report. The historical selected financial information may not be indicative of our future performance and should be read in conjunction with the information contained in Management’s Discussion and Analysis of Financial Condition and Results of Operations, and the Consolidated Financial Statements and the accompanying Notes to the Consolidated Financial Statements in this report.
| Twelve Months Ended December 31, | |||||||||||||||||||
| 2018 (1) (2) | 2017 (3) (4) | 2016 (5) | 2015 (6) (7) | 2014 (8) | |||||||||||||||
| (In millions, except per share data) | |||||||||||||||||||
| Summary of Operations: | |||||||||||||||||||
| Operating revenue | $ | 3,412.1 | $ | 3,362.2 | $ | 3,144.9 | $ | 2,663.6 | $ | 2,436.4 | |||||||||
| Operating expenses | 2,964.1 | 2,530.5 | 2,319.8 | 1,963.6 | 1,794.5 | ||||||||||||||
| Operating income | 448.0 | 831.7 | 825.1 | 700.0 | 641.9 | ||||||||||||||
| Consolidated income from continuing operations | 306.3 | 598.0 | 495.1 | 434.8 | 374.0 | ||||||||||||||
| Net income attributable to Equifax | $ | 299.8 | $ | 587.3 | $ | 488.8 | $ | 429.1 | $ | 367.4 | |||||||||
| Dividends paid to Equifax shareholders | $ | 187.9 | $ | 187.4 | $ | 157.6 | $ | 137.8 | $ | 121.2 | |||||||||
| Diluted earnings per share | |||||||||||||||||||
| Net income attributable to Equifax | $ | 2.47 | $ | 4.83 | $ | 4.04 | $ | 3.55 | $ | 2.97 | |||||||||
| Cash dividends declared per share | $ | 1.56 | $ | 1.56 | $ | 1.32 | $ | 1.16 | $ | 1.00 | |||||||||
| Weighted-average shares outstanding (diluted) | 121.4 | 121.5 | 121.1 | 120.9 | 123.5 |
| As of December 31, | |||||||||||||||||||
| 2018 (1) (2) | 2017 (3) (4) | 2016 (5) | 2015 (6) (7) | 2014 (8) | |||||||||||||||
| (In millions) | |||||||||||||||||||
| Balance Sheet Data: | |||||||||||||||||||
| Total assets | $ | 7,153.2 | $ | 7,233.4 | $ | 6,664.0 | $ | 4,501.5 | $ | 4,661.0 | |||||||||
| Short-term debt and current maturities | 4.9 | 965.3 | 585.4 | 49.3 | 380.4 | ||||||||||||||
| Long-term debt, net of current portion | 2,630.6 | 1,739.0 | 2,086.8 | 1,138.4 | 1,145.7 | ||||||||||||||
| Total debt, net | 2,635.5 | 2,704.3 | 2,672.2 | 1,187.7 | 1,526.1 | ||||||||||||||
| Total equity | 3,155.7 | 3,239.0 | 2,721.3 | 2,350.4 | 2,234.6 |
| (1) | During the year ended December 31, 2018, the Company recorded $401.2 million of pre-tax expenses related to the 2017 cybersecurity incident and insurance recoveries of $75.0 million for net expenses of $326.2 million. Costs related to the 2017 cybersecurity incident are defined as incremental costs to transform our information technology infrastructure and data security; legal fees and professional services costs to investigate the 2017 cybersecurity incident and respond to legal, government and regulatory claims; as well as costs to provide the free product and related support to the consumer. |
| (2) | During the fourth quarter of 2018, we recorded a restructuring charge of $46.1 million all of which is recorded in selling, general, and administrative expenses in our Consolidated Statements of Income. The restructuring charge primarily relates to a reduction in headcount to support the Company’s strategic objectives and increase the integration of our global operations. For additional information, see Note 11 of the Notes to the Consolidated Financial Statements in this report. |
| (3) | During the year ended December 31, 2017, the Company recorded $164.0 million of pre-tax expenses related to the 2017 cybersecurity incident and insurance recoveries of $50.0 million for net expenses of $114.0 million. Expenses include costs to investigate and remediate the 2017 cybersecurity incident and legal and other professional services related thereto, all of which were expensed as incurred. Additionally, as a result of the 2017 cybersecurity incident, we offered free credit file monitoring and identity theft protection to all U.S. consumers. We recorded the expenses necessary to provide this service to those who signed up during 2017. For additional information, see Note 6 of the Notes to the Consolidated Financial Statements in this report. |
| (4) | The Tax Cuts and Jobs Act of 2017 (“Tax Act”), as signed by the President of the United States on December 22, 2017, significantly revised U.S. tax law. The legislation positively impacted the Company’s ongoing effective tax rate due to the reduction of the U.S. federal corporate tax rate from 35% to 21%. The Tax Act made major changes to the U.S. international tax system. Under previous law, foreign earnings were subject to U.S. tax when repatriated to the U.S. Under the Tax Act, foreign earnings are generally exempt from U.S. tax. Additionally, there is a one-time deemed repatriation tax on undistributed foreign earnings and profits (the “transition tax”). The Tax Act imposes other U.S. taxes on “global intangible low taxed income” and “base erosion anti-abuse transactions.” Other significant changes included limitations on the deductibility of interest expense and executive compensation, and repeal of the deduction for domestic production activities. As a result of the current interpretation and estimated impact of the Tax Act, the Company recorded adjustments totaling a net tax benefit of $48.3 million in the fourth quarter of 2017 to provisionally account for the estimated impact. Refer to Note 7 of the Notes to the Consolidated Financial Statements in this Form 10-K for additional information. We also prospectively applied the provisions of ASU 2016-09 “Compensation - Stock Compensation (Topic 718),” related to the recognition of windfall tax benefits in the Consolidated Statement of Income which resulted in the recognition of $26.7 million of tax benefits for the year ended December 31, 2017. |
| (5) | In the first quarter of 2016, we completed the acquisition of 100% of the ordinary voting shares of Veda for cash consideration plus debt assumed of approximately $1.9 billion. For the year ended December 31, 2016, we recorded $40.2 million ($28.2 million, net of tax) for Veda acquisition related amounts. Of this amount, $30.1 million relates to transaction and integration costs in operating income, $9.2 million is recorded in other income and is the impact of foreign currency changes on the transaction structure, including the economic hedges, $0.2 million is recorded in depreciation and amortization, and $0.7 million is recorded in interest expense. |
| (6) | In the first quarter of 2015, we recorded a $20.7 million restructuring charge ($13.2 million, net of tax) all of which was recorded in selling, general and administrative expenses on our Consolidated Statements of Income. This charge resulted from our continuing efforts to realign our internal resources to support the Company’s strategic objectives and increase the integration of our global operations. |
| (7) | During the second quarter of 2015, the management of Boa Vista Servicos S.A. (“BVS”), in which we hold a 15% cost method investment, updated the financial projections of BVS. The updated projections, along with the continued weakness in the Brazilian consumer and small commercial credit markets were considered indicators of impairment. As a result of these changes, and the associated near-term changes in cash flow expected from the business, we recorded a 46.0 million Brazilian Reais ($14.8 million) impairment of our investment. |
| (8) | During the first quarter of 2014, we acquired 100% of the stock of TDX, a data, technology and services company in the United Kingdom that specializes in debt collections and recovery management through the use of analytics, data exchanges and technology platforms. The results of this acquisition have been included in our USIS and International operating segments subsequent to the acquisition. |
Item 7. MANAGEMENT’S DISCUSSION AND ANALYSIS OF FINANCIAL CONDITION AND RESULTS OF OPERATIONS
As used herein, the terms Equifax, the Company, we, our and us refer to Equifax Inc., a Georgia corporation, and its consolidated subsidiaries as a combined entity, except where it is clear that the terms mean only Equifax Inc.
All references to earnings per share data in Management’s Discussion and Analysis, or MD&A, are to diluted earnings per share, or EPS, unless otherwise noted. Diluted EPS is calculated to reflect the potential dilution that would occur if stock options or other contracts to issue common stock were exercised and resulted in additional common shares outstanding.
BUSINESS OVERVIEW
Equifax Inc. is a global data, analytics and technology company. We provide information solutions and human resources business process outsourcing services for businesses, governments and consumers. We have a large and diversified group of clients, including financial institutions, corporations, governments and individuals. Our services are based on comprehensive databases of consumer and business information derived from numerous sources including credit, financial assets, telecommunications and utility payments, employment, income, demographic and marketing data. We use advanced statistical techniques, machine learning and proprietary software tools to analyze available data to create customized insights, decision-making solutions and processing services for our clients. We also provide information, technology and services to support debt collections and recovery management. Additionally, we are a leading provider of payroll-related and human resource management business process outsourcing services in the United States of America, or U.S. For consumers, we provide products and services to help people understand, manage and protect their personal information and make more informed financial decisions.
We currently operate in four global regions: North America (U.S. and Canada), Asia Pacific (Australia, New Zealand and India), Europe (the United Kingdom, or U.K., Spain and Portugal) and Latin America (Argentina, Chile, Costa Rica, Ecuador, El Salvador, Honduras, Mexico, Paraguay, Peru and Uruguay). We maintain support operations in the Republic of Ireland, Chile, Costa Rica and India. We also offer Equifax branded credit services in Russia and India through joint ventures, have investments in consumer and/or commercial credit information companies through joint ventures in Cambodia, Malaysia, Singapore and the United Arab Emirates, and have an investment in a consumer and commercial credit information company in Brazil.
2017 Cybersecurity Incident
In 2017, we experienced a cybersecurity incident following a criminal attack on our systems that involved the theft of certain personally identifiable information of U.S., Canadian and U.K. consumers. Criminals exploited a software vulnerability in a U.S. website application to gain unauthorized access to our network. In March 2017, the U.S. Department of Homeland Security distributed a notice concerning the software vulnerability. We undertook efforts to identify and remediate vulnerable systems; however, the vulnerability in the website application that was exploited was not identified by our security processes. We discovered unusual network activity in late-July 2017 and upon discovery promptly investigated the activity. Once the activity was identified as potential unauthorized access, we acted to stop the intrusion and engaged a leading, independent cybersecurity firm to conduct a forensic investigation to determine the scope of the unauthorized access, including the specific information impacted. Based on our forensic investigation, the unauthorized access occurred from mid-May 2017 through July 2017. No evidence was found that the Company’s core consumer, employment and income, or commercial reporting databases were accessed. We continue to cooperate with law enforcement in connection with the criminal investigation into the actors responsible for the 2017 cybersecurity incident.
As a result of the 2017 cybersecurity incident, we are party to numerous lawsuits and governmental investigations. See “Item 1A. Risk Factors” and “Item 3. Legal Proceedings” in this Form 10-K for more information regarding these lawsuits and investigations.
Product Liability. As a result of the 2017 cybersecurity incident, we offered TrustedID® Premier, a credit file monitoring and identity theft protection product, for free to all eligible U.S. consumers who signed up through January 31, 2018. We also provided free credit reports and scores, credit monitoring and identity theft protection for twenty four months to impacted consumers in Canada and the U.K. We have recorded the expenses necessary to provide this service to those who signed up. Through December 31, 2017, we recorded $50.7 million of product costs in selling, general and administrative expenses in the accompanying Consolidated Statements of Income. In 2018, the Company extended the free credit monitoring services for an additional twelve months for eligible consumers impacted by the 2017 cybersecurity incident by providing them the opportunity to enroll in Experian® IDNotify™ at no cost. We recorded $20.4 million related to these services in selling,
general, and administrative expenses in the accompanying Consolidated Statements of Income for the twelve months ended December 31, 2018.
Litigation, Claims and Government Investigations. As a result of the 2017 cybersecurity incident, we are subject to a significant number of proceedings and investigations as described in Part I, “Item 3. Legal Proceedings” in this Form 10-K. While we believe it is reasonably possible that we will incur losses associated with such proceedings and investigations, it is not possible at this time to estimate the amount of loss or range of possible loss that might result from adverse judgments, settlements, penalties or other resolution of the proceedings and investigations described in “Item 3. Legal Proceedings” based on the various stages of these proceedings and investigations, that alleged damages have not been specified or are uncertain, the uncertainty as to the certification of a class or classes and the size of any certified class, as applicable, and the lack of resolution on significant factual and legal issues. The Company will continue to evaluate information as it becomes known and will record an estimate for losses at the time or times when it is both probable that a loss has been incurred and the amount of the loss is reasonably estimable. The Company believes that the ultimate amount paid on these actions, claims and investigations could be material to the Company’s consolidated financial condition, results of operations, or cash flows in future periods.
Future Costs. We are currently executing substantial initiatives in security and consumer support, and a company-wide transformation of our technology infrastructure, which we refer to as our technology transformation, and incurred substantial increased expenses and capital expenditures in 2018 related to these initiatives. We expect to again incur significant expenses and capital expenditures in 2019 and 2020 related to these initiatives, although at levels slightly below those incurred in 2018.
We incurred significant legal and professional services expenses related to the lawsuits, claims and government investigations to which we are a party in 2018, and expect to continue to incur these expenses until these items are resolved. We will recognize the expenses and capital expenditures referenced herein as they are incurred. In 2018, we incurred elevated costs for insurance, finance and compliance activities, and expect to incur costs at these levels again in 2019.
Insurance Coverage. At the time of the 2017 cybersecurity incident, we had $125.0 million of cybersecurity insurance coverage, above a $7.5 million deductible, to limit our exposure to losses such as those related to this incident. During the t
Showing the first 8K of 112K characters. Open the full section
Item 7A. QUANTITATIVE AND QUALITATIVE DISCLOSURES ABOUT MARKET RISK
In the normal course of our business, we are exposed to market risk, primarily from changes in foreign currency exchange rates and interest rates that could impact our results of operations and financial position. We manage our exposure to these market risks through our regular operating and financing activities, and, when deemed appropriate, through the use of derivative financial instruments, such as interest rate swaps, to hedge certain of these exposures. We use derivative financial instruments as risk management tools and not for speculative or trading purposes.
Foreign Currency Exchange Rate Risk
A substantial majority of our revenue, expense and capital expenditure activities are transacted in U.S. dollars. However, we do transact business in other currencies, primarily the British pound, the Australian dollar, the Canadian dollar, the Chilean peso, the Argentine peso and the Euro. For most of these foreign currencies, we are a net recipient, and, therefore, benefit from a weaker U.S. dollar and are adversely affected by a stronger U.S. dollar relative to the foreign currencies in which we transact significant amounts of business.
We are required to translate, or express in U.S. dollars, the assets and liabilities of our foreign subsidiaries that are denominated or measured in foreign currencies at the applicable year-end rate of exchange on our Consolidated Balance Sheets and income statement items of our foreign subsidiaries at the average rates prevailing during the year. We record the resulting translation adjustment, and gains and losses resulting from the translation of intercompany balances of a long-term investment nature within other comprehensive income, as a component of our shareholders’ equity. Foreign currency transaction gains and losses, which have historically been immaterial, are recorded on our Consolidated Statements of Income. We generally do not mitigate the risks associated with fluctuating exchange rates, although we may from time to time through forward contracts or other derivative instruments hedge a portion of our translational foreign currency exposure or exchange rate risks associated with material transactions which are denominated in a foreign currency.
For the year ended December 31, 2018, a 10% weaker U.S. dollar against the currencies of all foreign countries in which we had operations during 2018 would have increased our revenue by $55.9 million and our pre-tax operating profit by $10.7 million. For the year ended December 31, 2017, a 10% weaker U.S. dollar against the currencies of all foreign countries in which we had operations during 2017 would have increased our revenue by $54.7 million and our pre-tax operating profit by $18.6 million. A 10% stronger U.S. dollar would have resulted in similar decreases to our revenue and pre-tax operating profit for 2018 and 2017.
On average across our mix of international businesses, foreign currencies at December 31, 2018 were weaker against the U.S. dollar than the average foreign exchange rates that prevailed across the full year 2018. As a result, if foreign exchange rates were unchanged throughout 2019, foreign exchange translation would reduce growth as reported in U.S. dollars. As foreign exchange rates change daily, there can be no assurance that foreign exchange rates will remain constant throughout 2019, and rates could go either higher or lower.
Interest Rate Risk
Our exposure to market risk for changes in interest rates relates to our variable-rate commercial paper, Revolver, and Floating Rate Senior Note borrowings. We attempt to achieve the lowest all-in weighted-average cost of debt while simultaneously taking into account the mix of our fixed- and floating-rate debt, and the average life and scheduled maturities of our debt. At December 31, 2018, our weighted average cost of debt was 3.8% and weighted-average life of debt was 5.42 years. At December 31, 2018, 89% of our debt was fixed rate, and the remaining 11% was variable rate. Occasionally we use derivatives to manage our exposure to changes in interest rates by entering into interest rate swaps. A 100 basis point increase in the weighted-average interest rate on our variable-rate debt would have increased our 2018 interest expense by $3.0 million.
Based on the amount of outstanding variable-rate debt, we have exposure to interest rate risk. In the future, if our mix of fixed-rate and variable-rate debt were to change due to additional borrowings under existing or new variable-rate debt, we could have additional exposure to interest rate risk. The nature and amount of our long-term and short-term debt, as well as the proportionate amount of fixed-rate and variable-rate debt, can be expected to vary as a result of future business requirements, market conditions and other factors.
Item 8. FINANCIAL STATEMENTS AND SUPPLEMENTARY DATA
Report of Independent Registered Public Accounting Firm
To the Shareholders and the Board of Directors of Equifax Inc.
Opinion on Internal Control over Financial Reporting
We have audited Equifax Inc.’s internal control over financial reporting as of December 31, 2018, based on criteria established in Internal Control-Integrated Framework issued by the Committee of Sponsoring Organizations of the Treadway Commission (“2013 framework”) (the COSO criteria). In our opinion, Equifax Inc. (the Company) maintained, in all material respects, effective internal control over financial reporting as of December 31, 2018, based on the COSO criteria.
We also have audited, in accordance with the standards of the Public Company Accounting Oversight Board (United States) (PCAOB), the consolidated balance sheets of the Company as of December 31, 2018 and 2017, the related consolidated statements of income, comprehensive income (loss), cash flows, and shareholders’ equity and other comprehensive income(loss) for each of the three years in the period ended December 31, 2018, and the related notes and financial statement schedule listed in the Index at Item 15(a)(2) (collectively referred to as the “consolidated financial statements”) and our report dated February 21, 2019 expressed an unqualified opinion thereon.
Basis for Opinion
The Company’s management is responsible for maintaining effective internal control over financial reporting and for its assessment of the effectiveness of internal control over financial reporting included in the accompanying Management’s Annual Report on Internal Control over Financial Reporting. Our responsibility is to express an opinion on the Company’s internal control over financial reporting based on our audit. We are a public accounting firm registered with the PCAOB and are required to be independent with respect to the Company in accordance with the U.S. federal securities laws and the applicable rules and regulations of the Securities and Exchange Commission and the PCAOB.
We conducted our audit in accordance with the standards of the PCAOB. Those standards require that we plan and perform the audit to obtain reasonable assurance about whether effective internal control over financial reporting was maintained in all material respects.
Our audit included obtaining an understanding of internal control over financial reporting, assessing the risk that a material weakness exists, testing and evaluating the design and operating effectiveness of internal control based on the assessed risk, and performing such other procedures as we considered necessary in the circumstances. We believe that our audit provides a reasonable basis for our opinion.
Definition and Limitations of Internal Control Over Financial Reporting
A company’s internal control over financial reporting is a process designed to provide reasonable assurance regarding the reliability of financial reporting and the preparation of financial statements for external purposes in accordance with generally accepted accounting principles. A company’s internal control over financial reporting includes those policies and procedures that (1) pertain to the maintenance of records that, in reasonable detail, accurately and fairly reflect the transactions and dispositions of the assets of the company; (2) provide reasonable assurance that transactions are recorded as necessary to permit preparation of financial statements in accordance with generally accepted accounting principles, and that receipts and expenditures of the company are being made only in accordance with authorizations of management and directors of the company; and (3) provide reasonable assurance regarding prevention or timely detection of unauthorized acquisition, use, or disposition of the company’s assets that could have a material effect on the financial statements.
Because of its inherent limitations, internal control over financial reporting may not prevent or detect misstatements. Also, projections of any evaluation of effectiveness to future periods are subject to the risk that controls may become inadequate because of changes in conditions, or that the degree of compliance with the policies or procedures may deteriorate.
/s/ Ernst & Young LLP
Atlanta, Georgia
February 21, 2019
Report of Independent Registered Public Accounting Firm
To the Shareholders and the Board of Directors of Equifax Inc.
Opinion on the Consolidated Financial Statements
We have audited the accompanying consolidated balance sheets of Equifax Inc. (the Company) as of December 31, 2018 and 2017, the related consolidated statements of income, comprehensive income(loss), cash flows, and shareholders’ equity and other comprehensive income(loss) for each of the three years in the period ended December 31, 2018, and the related notes and financial statement schedule listed in the Index at Item 15(a)(2) (collectively referred to as the “consolidated financial statements”). In our opinion, the consolidated financial statements present fairly, in all material respects, the financial position of the Company at December 31, 2018 and 2017, and the results of its operations and its cash flows for each of the three years in the period ended December 31, 2018, in conformity with U.S. generally accepted accounting principles.
We also have audited, in accordance with the standards of the Public Company Accounting Oversight Board (United States) (PCAOB), the Company’s internal control over financial reporting as of December 31, 2018, based on criteria established in Internal Control-Integrated Framework issued by the Committee of Sponsoring Organizations of the Treadway Commission (2013 framework) and our report dated February 21, 2019 expressed an unqualified opinion thereon.
Basis for Opinion
These consolidated financial statements are the responsibility of the Company’s management. Our responsibility is to express an opinion on the Company’s consolidated financial statements based on our audits. We are a public accounting firm registered with the PCAOB and are required to be independent with respect to the Company in accordance with the U.S. federal securities laws and the applicable rules and regulations of the Securities and Exchange Commission and the PCAOB.
We conducted our audits in accordance with the standards of the PCAOB. Those standards require that we plan and perform the audit to obtain reasonable assurance about whether the consolidated financial statements are free of material miss
Showing the first 8K of 236K characters. Open the full section
Item 9. CHANGES IN AND DISAGREEMENTS WITH ACCOUNTANTS ON ACCOUNTING AND FINANCIAL DISCLOSURE
None.
Item 9A. CONTROLS AND PROCEDURES
Evaluation of Disclosure Controls and Procedures
Our management, with the participation of our Chief Executive Officer and Chief Financial Officer, evaluated the effectiveness of Equifax’s disclosure controls and procedures as of the end of the period covered by this report. Based on that evaluation, our Chief Executive Officer and Chief Financial Officer concluded that our disclosure controls and procedures as of the end of the period covered by this report (i) were appropriately designed to provide reasonable assurance of achieving their objectives and (ii) were effective and provided reasonable assurance that the information required to be disclosed by Equifax in reports filed under the Exchange Act is (a) recorded, processed, summarized and reported within the time periods specified in the SEC’s rules and forms and (b) accumulated and communicated to Equifax’s management, including our Chief Executive Officer and Chief Financial Officer, as appropriate to allow timely decisions regarding required disclosure.
Management’s Annual Report on Internal Control Over Financial Reporting
Our management is responsible for establishing and maintaining adequate internal control over financial reporting. Internal control over financial reporting is defined in Rules 13a-15(f) and 15d-15(f) under the Exchange Act as a process designed by, or under the supervision of, our Chief Executive Officer and Chief Financial Officer and effected by our Board of Directors, management and other personnel, to provide reasonable assurance regarding the reliability of financial reporting and the preparation of financial statements for external purposes in accordance with generally accepted accounting principles and includes those policies and procedures that:
| • | pertain to the maintenance of records that in reasonable detail accurately and fairly reflect transactions and dispositions of our assets; |
| • | provide reasonable assurance that transactions are recorded as necessary to permit preparation of financial statements in accordance with generally accepted accounting principles, and that our receipts and expenditures are being made only in accordance with authorizations of our management and directors; and |
| • | provide reasonable assurance regarding prevention or timely detection of unauthorized acquisition, use or disposition of our assets that could have a material effect on the financial statements. |
Because of its inherent limitations, internal control over financial reporting may not prevent or detect misstatements. Projections of any evaluation of effectiveness to future periods are subject to the risk that controls may become inadequate because of changes in conditions, or that the degree of compliance with the policies or procedures may deteriorate.
Our management assessed the effectiveness of Equifax’s internal control over financial reporting as of December 31, 2018 using the criteria set forth by the Committee of Sponsoring Organizations of the Treadway Commission (COSO) in Internal Control-Integrated Framework (2013 Framework). Based on this assessment using those criteria, our management concluded that, as of December 31, 2018, Equifax’s internal control over financial reporting was effective. Management reviewed the results of its assessment with the Audit Committee of its Board of Directors. The effectiveness of Equifax’s internal control over financial reporting as of December 31, 2018 has been audited by Ernst & Young LLP, Equifax’s independent registered public accounting firm, as stated in their report, which appears in “Item 8. Financial Statements and Supplementary Data” of this Form 10-K on page 60.
Changes in Internal Control Over Financial Reporting
There have been no changes in internal control over financial reporting identified in connection with the foregoing that have materially affected, or are reasonably likely to materially affect, our internal control over financial reporting.
Item 9B. OTHER INFORMATION
None.
PART III
Item 10. DIRECTORS, EXECUTIVE OFFICERS AND CORPORATE GOVERNANCE
Except for the information about our executive officers shown below, the information required by this Item 10 is incorporated herein by reference from the information contained in our Proxy Statement to be filed with the SEC in connection with the solicitation of proxies for our 2019 Annual Meeting of Shareholders (the “2019 Proxy Statement”) under the sections entitled “Proposal 1 Election of Directors,” “Section 16(a) Beneficial Ownership Reporting Compliance” and “Board Leadership and Corporate Governance—Committees of the Board of Directors.”
We have adopted a written Code of Ethics and Business Conduct applicable to all our employees, including our principal executive officer, principal financial officer, and principal accounting officer and controller, and to members of our Board of Directors. Our Code of Ethics and Business Conduct is available on our investor relations website: www.equifax.com/about-equifax/corporate-governance. We will disclose amendments to certain provisions of our Code of Ethics and Business Conduct, or waivers of such provisions granted to executive officers and directors, on this website.
Executive Officers
Information regarding the executive officers of Equifax Inc. is set forth below.
Mark W. Begor (60) has been Chief Executive Officer and a member of the Board of Directors since April 2018. Prior thereto, he was a Managing Director in the Industrial and Business Services group at Warburg Pincus, a global private equity investment firm, since June 2016. Prior to Warburg Pincus, Mr. Begor spent 35 years at General Electric Company (“GE”), a global industrial and financial services company, in a variety of operating and financial roles. During his career at GE, Mr. Begor served in a variety of roles leading multibillion dollar units of the company, including President and CEO of GE Energy Management from 2014 to 2016, President and CEO of GE Capital Real Estate from 2011 to 2014, and President and CEO of GE Capital Retail Finance (Synchrony Financial) from 2002 to 2011. Mr. Begor served on the Fair Isaac Corporation (FICO) Board of Directors from 2016 to 2018.
J. Dann Adams (61) has been President, Global Consumer Solutions, since November 2015. Prior thereto, he served as President, Workforce Solutions, since July 2010. Prior thereto, he served as President, U.S. Information Solutions from 2007 to June 2010. Prior thereto, he served as Group Executive, North America Information Services from November 2003 until December 2006.
Jamil Farshchi (41) has been our Chief Information Security Officer since February 2018. Prior to joining Equifax, Mr. Farshchi served as Chief Information Security Officer at The Home Depot since April 2015. Prior thereto, he was the first Global Chief Information Security Officer at Time Warner Inc., from August 2014 to March 2015. Prior thereto, he was the Vice President of Global Information Security at Visa Inc. from August 2011 to August 2014. Mr. Farshchi has also held senior roles at Los Alamos National Laboratory, Sitel Corporation, Nextwave Broadband and NASA.
John W. Gamble, Jr. (56) has been Corporate Vice President and Chief Financial Officer since May 2014. Prior to that, Mr. Gamble was Executive Vice President and Chief Financial Officer of Lexmark International, Inc., a global provider of document solutions, enterprise content management software and services, printers and multifunction printers, from September 2005 until May 2014.
John T. Hartman (59) has been President, International, since November 2015. Prior thereto, he served as Senior Vice President, Corporate Development, since April 2010. Prior thereto, he served as President of Growth Vector from 2009 to 2010. Prior thereto, he served as Executive Vice President and Chief Commercial Officer for Acuity Brands from 2004 to 2009.
Julia A. Houston (48) has been Chief Transformation Officer since October 2017. Prior thereto, she was Senior Vice President, U.S. Legal, since October 2013. Prior to joining Equifax, Ms. Houston was Senior Vice President, General Counsel and Corporate Secretary at Convergys Corporation, from 2011 to 2013. Prior thereto, she served in roles of increasing responsibility at Mirant Corporation from 2004 to 2010, ultimately serving as Senior Vice President, General Counsel, Chief Compliance Officer and Corporate Secretary.
John J. Kelley III (58) has been Corporate Vice President and Chief Legal Officer since January 2013. Prior to joining Equifax, Mr. Kelley was a senior partner in the Corporate Practice Group of the law firm of King & Spalding LLP from January 1993 to December 2012.
Bryson Koehler (43) has been our Chief Technology Officer since June 2018. Prior to joining Equifax, Mr. Koehler served as Chief Technology Officer of IBM Watson and Cloud Platform since November 2016. Prior to that, Mr. Koehler was Chief Technology and Information Officer of The Weather Channel Companies, before it was acquired in 2015 by IBM. Before that, he served as Senior Vice President of Global Revenue & Guest Technology at the Intercontinental Hotels Group.
Rodolfo O. Ploder (58) has been President, Workforce Solutions, since November 2015. Prior thereto, he served as President, U.S. Information Solutions, since April 2010. Prior thereto, he served as President, International, from January 2007 to April 2010. Prior thereto, he was Group Executive, Latin America from February 2004 to January 2007.
Coretha M. Rushing (62) has been Corporate Vice President and Chief Human Resources Officer since 2006. Prior to joining Equifax, she served as an executive coach and HR Consultant with Atlanta-based Cameron Wesley LLC. Prior thereto, she was Senior Vice President of Human Resources at The Coca-Cola Company, where she was employed from 1996 until 2004.
Sid Singh (41) has been President, U.S. Information Solutions, since February 11, 2019. Mr. Singh served as group president of Integrated Solutions & Vertical Markets at Global Payments Inc., since February 2013. Prior thereto, he served as Senior Vice President, Global Product of Global Payments Inc. since 2010. Prior thereto, he served as Vice President and Regional Head, Asia Pacific of Global Payments Inc. since 2006. Prior thereto, he held senior management positions with HSBC and Citibank.
Laura L. Wilbanks (51) has been Chief Marketing Officer since August 2017. Prior thereto, she served as Senior Vice President and Senior Marketing Officer for U.S. Information Solutions, since May 2013. Prior thereto, she served as Senior Vice President, Strategic Marketing since January 2010. Prior thereto, since February 1998, Ms. Wilbanks held positions of increasing responsibility at Equifax, including leadership roles in global product management, global strategy, market development and market insight and planning.
Item 11. EXECUTIVE COMPENSATION
The information required by this Item 11 is incorporated herein by reference from the information contained in our 2019 Proxy Statement under the sections entitled “Executive Compensation” and “Director Compensation.”
Item 12. SECURITY OWNERSHIP OF CERTAIN BENEFICIAL OWNERS AND MANAGEMENT AND RELATED STOCKHOLDER MATTERS
The information required by this Item 12 is incorporated herein by reference from the information contained in our 2019 Proxy Statement under the sections entitled “Security Ownership of Management and Certain Beneficial Owners” and “Executive Compensation Equity Compensation Plan Information.”
Item 13. CERTAIN RELATIONSHIPS AND RELATED TRANSACTIONS AND DIRECTOR INDEPENDENCE
The information required by this Item 13 is incorporated herein by reference from the information contained in our 2019 Proxy Statement under the sections entitled “Board Leadership and Corporate Governance Director Independence, ” “Related Person Transaction Policy” and “Certain Relationships and Related Person Transactions of Directors, Executive Officers, and 5 Percent Shareholders.”
Item 14. PRINCIPAL ACCOUNTANT FEES AND SERVICES
The information required by this Item 14 is incorporated herein by reference from the information contained in our 2019 Proxy Statement under the section entitled “Proposal 3 Ratification of Appointment of Ernst & Young LLP as Independent Registered Public Accounting Firm for 2019.”
PART IV
Item 15. EXHIBITS AND FINANCIAL STATEMENT SCHEDULES
| (a) | List of Documents Filed as a Part of This Report: |
| (1) | Financial Statements. The following financial statements are included in Item 8 of Part II: |
| • | Consolidated Balance Sheets — December 31, 2018 and 2017; |
| • | Consolidated Statements of Income for the Years Ended December 31, 2018, 2017 and 2016; |
| • | Consolidated Statements of Comprehensive Income for the Years Ended December 31, 2018, 2017 and 2016; |
| • | Consolidated Statements of Cash Flows for the Years Ended December 31, 2018, 2017 and 2016; |
| • | Consolidated Statements of Shareholders’ Equity and Other Comprehensive Income for the Years Ended December 31, 2018, 2017 and 2016; and |
| • | Notes to Consolidated Financial Statements. |
| (2) | Financial Statement Schedules. |
- Schedule II — Valuation and Qualifying Accounts
All other schedules for which provision is made in the applicable accounting regulation of the SEC are not required under the related instructions or are inapplicable and, therefore, have been omitted.
| (3) | Exhibits. See exhibits listed under Part (b) below. |
(b) Exhibits:
- Filed herewith
(c) Financial Statement Schedules. See Item 15(a)(2).
Item 16. FORM 10-K SUMMARY
None.
SIGNATURES
Pursuant to the requirements of Section 13 or 15(d) of the Securities Exchange Act of 1934, the registrant has duly caused this report to be signed on its behalf by the undersigned, thereunto duly authorized, on February 21, 2019.
| EQUIFAX INC. | |
| (Registrant) | |
| By: | /s/ Mark W. Begor |
| Mark W. Begor | |
| Chief Executive Officer |
We, the undersigned directors and executive officers of Equifax Inc., hereby severally constitute and appoint John W. Gamble, Jr. and James M. Griggs, and each of them singly, our true and lawful attorneys with full power to them and each of them to sign for us, and in our names in the capacities indicated below, any and all amendments to this Annual Report on Form 10-K filed with the SEC, hereby ratifying and confirming our signatures as they may be signed by our said attorneys to any and all amendments to said Annual Report on Form 10-K.
Pursuant to the requirements of the Securities Exchange Act of 1934, this report has been signed below by the following persons on behalf of the registrant and in the capacities indicated on February 21, 2019.
| /s/ Mark W. Begor | |
| Mark W. Begor | |
| Chief Executive Officer | |
| (Principal Executive Officer) | |
| /s/ John W. Gamble, Jr. | |
| John W. Gamble, Jr. | |
| Corporate Vice President and Chief Financial Officer | |
| (Principal Financial Officer) | |
| /s/ James M. Griggs | |
| James M. Griggs | |
| Chief Accounting Officer and Corporate Controller | |
| (Principal Accounting Officer) | |
| /s/ Mark L. Feidler | |
| Mark L. Feidler | |
| Director and Non-Executive Chairman | |
| /s/ G. Thomas Hough | |
| G. Thomas Hough | |
| Director | |
| /s/ Robert D. Marcus | |
| Robert D. Marcus | |
| Director | |
| /s/ Siri S. Marshall | |
| Siri S. Marshall | |
| Director | |
| /s/ Scott A. McGregor | |
| Scott A. McGregor | |
| Director |
| /s/ John A. McKinley | |
| John A. McKinley | |
| Director | |
| /s/ Robert W. Selander | |
| Robert W. Selander | |
| Director | |
| /s/ Elane B. Stock | |
| Elane B. Stock | |
| Director |
SCHEDULE II — VALUATION AND QUALIFYING ACCOUNTS
2018
| Column A | Column B | Column C | Column D | Column E | ||||||||||||||||
| Additions | ||||||||||||||||||||
| Description | Balance at Beginning of Period | Charged to Costs and Expenses | Charged to Other Accounts | Deductions | Balance at End of Period | |||||||||||||||
| (In millions) | ||||||||||||||||||||
| Reserves deducted in the balance sheet from the assets to which they apply: | ||||||||||||||||||||
| Trade accounts receivable | $ | 9.1 | $ | 5.6 | $ | — | $ | (3.8 | ) | $ | 10.9 | |||||||||
| Deferred income tax asset valuation allowance | 401.8 | (164.0 | ) | (12.3 | ) | 206.4 | 431.9 | |||||||||||||
| $ | 410.9 | $ | (158.4 | ) | $ | (12.3 | ) | $ | 202.6 | $ | 442.8 |
2017
| Column A | Column B | Column C | Column D | Column E | ||||||||||||||||
| Additions | ||||||||||||||||||||
| Description | Balance at Beginning of Period | Charged to Costs and Expenses | Charged to Other Accounts | Deductions | Balance at End of Period | |||||||||||||||
| (In millions) | ||||||||||||||||||||
| Reserves deducted in the balance sheet from the assets to which they apply: | ||||||||||||||||||||
| Trade accounts receivable | $ | 7.8 | $ | 5.0 | $ | — | $ | (3.7 | ) | $ | 9.1 | |||||||||
| Deferred income tax asset valuation allowance | 307.3 | (6.1 | ) | 8.1 | 92.5 | 401.8 | ||||||||||||||
| $ | 315.1 | $ | (1.1 | ) | $ | 8.1 | $ | 88.8 | $ | 410.9 |
2016
| Column A | Column B | Column C | Column D | Column E | ||||||||||||||||
| Additions | ||||||||||||||||||||
| Description | Balance at Beginning of Period | Charged to Costs and Expenses | Charged to Other Accounts | Deductions | Balance at End of Period | |||||||||||||||
| (In millions) | ||||||||||||||||||||
| Reserves deducted in the balance sheet from the assets to which they apply: | ||||||||||||||||||||
| Trade accounts receivable | $ | 7.5 | $ | 2.2 | $ | — | $ | (1.9 | ) | $ | 7.8 | |||||||||
| Deferred income tax asset valuation allowance | 222.9 | (233.7 | ) | 23.8 | 294.3 | 307.3 | ||||||||||||||
| $ | 230.4 | $ | (231.5 | ) | $ | 23.8 | $ | 292.4 | $ | 315.1 |